Download the latest Vulnerability & Exploitation Report

Download now
CrowdSecBlocklists

Curated IP threat feeds your firewall pulls automatically

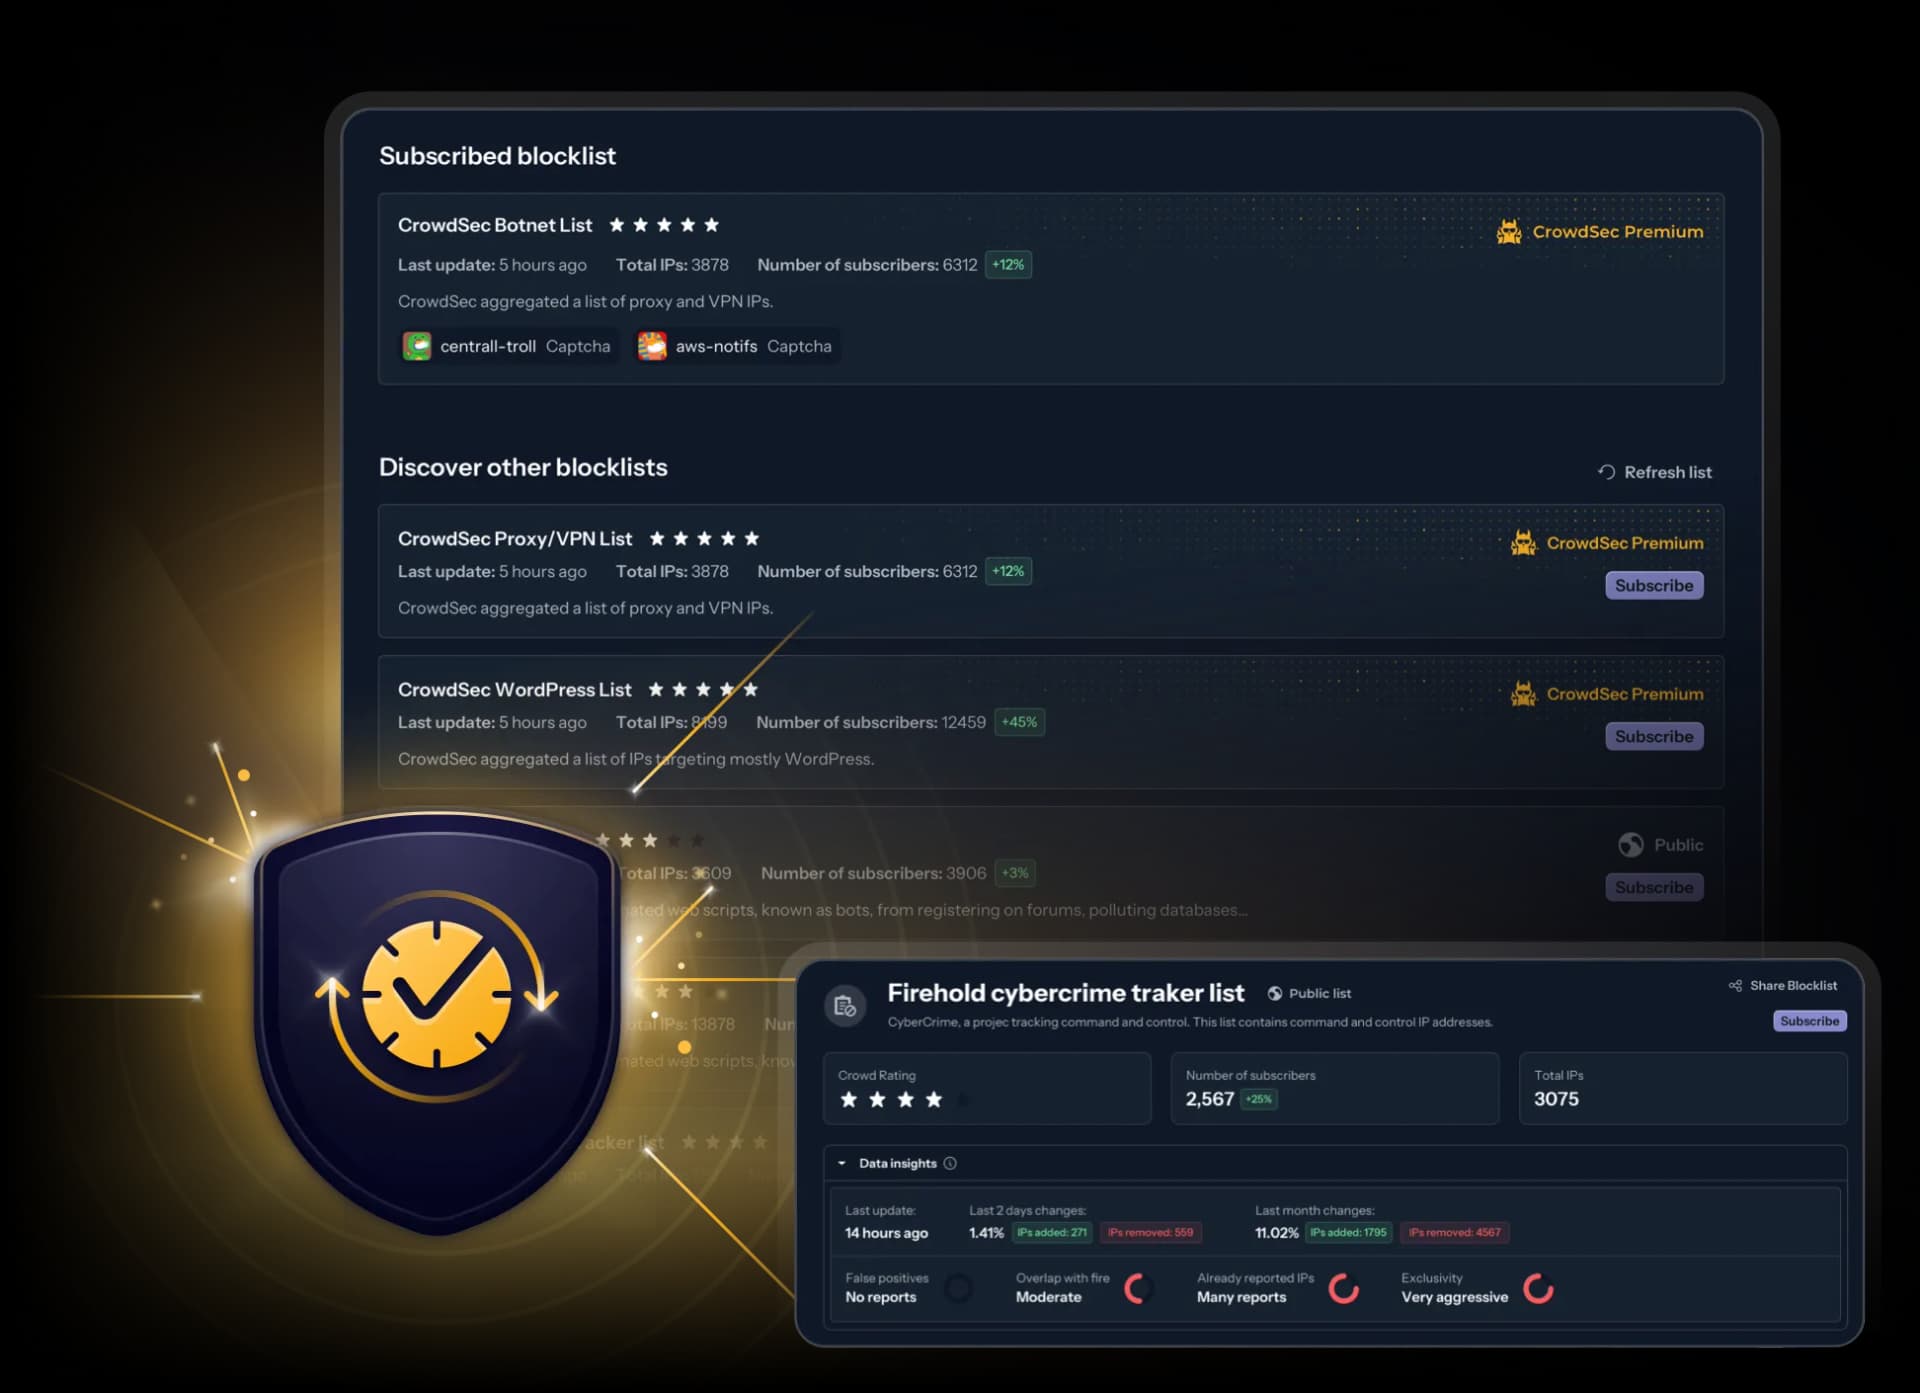
CrowdSec Blocklists are curated IP threat feeds: lists of IPs that are attacking right now, which your firewall, CDN or proxy pulls on its own. Plug them in as a Palo Alto External Dynamic List, a FortiGate threat feed, a Check Point IoC feed, a Cisco Security Intelligence feed, a Juniper dynamic address feed or a Sophos third-party threat feed, in minutes and with no agent to install. The lists are built from more than 40 million attack signals a day from 500,000 servers, and come by industry, country or attack type.

G2 reviews
87 Reviews
Blocklist hero

Not Just Another Blocklist

  • Overblocking IPs?

    Honeypots and third-party blocklists provide insufficient updates, resulting in cleared IPs remaining on blocklists and new infections taking longer to be added.

    With a 5% daily rotation on average, you won’t get any of that with CrowdSec.

  • High False Positives?

    We shield our data against false positives and poisoning using a combination of methods, including:

    • Reporter trust score and diversity
    • Machine profiling
    • Cross-checking data sources to guarantee information consistency
    • and more…
  • No VPN/Residential Proxy Detection?

    An efficient blocklist offers more than just a list of unwanted IPs.

    We employ behavior analysis on the data collected from the CrowdSec Network to provide you with ultra-curated lists — DDoS, botnets, VPNs, residential proxies, and more — to equip you with the intelligence you need to safeguard your services.

  • Infrequent Updates?

    CrowdSec Blocklists offer an average of 5% daily rotation of IPs.

    They are updated in real time and at top priority, providing you with fresh and relevant data daily and ensuring that the list of IPs you feed to your firewall is never out of date.

CrowdSec Blocklists Are Unique

Up to 80%

reduction in security alarm volume. Measured by our customers after using CrowdSec blocklists.

0%

false positives in the CrowdSec Blocklists, thanks to our unique curation process.

36%

Of proven aggressive IPs that CrowdSec proactively blocks are unknown to any other vendor for at least a week.

5%

daily rotation of malicious IPs on average in the CrowdSec Intelligence Blocklist.

7to60

days on average ahead in adding malicious IPs to our blocklists compared to others list on the market

16%

Of proven aggressive IPs that CrowdSec proactively blocks are still unknown to any other vendor for at least 15-20 days.

Wondering how we collect, analyze, and curate data?

Learn more about our data

Blocking Unwanted IPs VS.Blocking Unwanted Behaviors

Blocking any and all aggressive IPs is a solid option. But blocking IPs based on unwanted behaviors that have the potential to harm your infrastructure, gives you greater flexibility and targeted protection for your perimeter.

Explore the crowd-powered and ultra-curated CrowdSec Blocklists

CrowdSec Intelligence Blocklist

Contains all IPs in our database that have been identified as actively aggressive, performing a wide variety of attacks. Proactively block these IPs if you don’t want to take any chances with malicious IPs potentially reaching your systems.

Industry and Service-Focused Attackers Blocklists

Contain IPs frequently attacking organizations in a specific sector. We currently cover Banking & Insurance, Healthcare, Hosting, MSSPs, Retail & Ecommerce, IT & Services. Block these IPs to reduce security alerts and establish a safer perimeter to protect critical systems.

Country-Focused Attackers Blocklists

Contain a CrowdSec-aggregated list of the most aggressive IPs specifically targeting entities in a specific country. Proactively block these IPs to reduce the volume of your security alerts and establish an overall safer perimeter.

High Background Noise Blocklist

Contains IPs identified as malicious or potential threats performing mass exploitation attempts contributing to your internet background noise and high volume of security alerts. Blocking these IPs can reduce your alert volume and save infrastructure resources.

HTTP Attackers Blocklists

Contain IPs that have been mainly reported for performing HTTP DoS attacks or HTTP exploitation attempts. Proactively block these IPs to prevent DoS and HTTP exploitation attempts on your systems and establish an overall safer perimeter.

Custom Blocklists

Do you need custom blocklists for specific use cases? We work with you to make sure you have the intelligence you need to safeguard your services.

Plug N’ Play with Immediate Benefits

Integrating the CrowdSec Blocklists into your infrastructure is simple, effortless, and fail-proof.

icons1

Generate a CrowdSec CTI API key via the CrowdSec Console

Get started
icons2

Implement the Blocklists as an automated blocking rules on your existing firewall or CDN

icons3

Enjoy an immediate reduction in security alerts and a decrease in operational costs

Boosting SOC Efficiency & Cutting Costs

We turn Crowd-Powered Intelligence into actionable blocklists to maximize the efficiency of your security operations and reduce your costs.

Be Proactive & Minimize Downtime

Proactively block known malicious IPs to avoid service downtime and potential data losses that can lead to a significant loss in revenue and customer trust, as well as regulatory fines.

block malicious ip

Reduce Server Load & Egress Costs

Proactively block offensive IP addresses and make sure your servers dedicate all their resources to serving customers rather than attackers.

block-ip

Optimize Incident Response Costs

Filter out background noise to reduce the number of security alerts at the SOC level by 80% and allow your security experts to focus on critical security events.

Want to get a glimpse of what efficient security operations look like?

Download our Guide to Cost-Effective Security Operations and learn how to maximize protection while reducing security & operational costs.

Download Now

Use the CrowdSec Blocklistswith Any Firewall or CDN

The CrowdSec Blocklists integrate with a large number of tools, making you security ecosystem more powerful and efficient.

  • AWS Network FirewallAWS Network Firewall
  • Azure FirewallAzure Firewall
  • (GCP) Network Firewall(GCP) Network Firewall
  • CloudflareCloudflare
  • MikroTik RouterOSMikroTik RouterOS
  • Windows FirewallWindows Firewall
  • Palo AltoPalo Alto
  • CISCOCISCO
  • FortinetFortinet
  • Check PointCheck Point

Frequently asked questions

How do I add a threat intelligence feed to my firewall?

Create an integration in the CrowdSec Console, subscribe it to the lists you want, then add the endpoint as an external list in your firewall (Palo Alto EDL, FortiGate threat feed, Check Point IoC feed, pfSense URL table…). It takes a few minutes and needs no agent.

Is a CrowdSec blocklist the same as a threat feed?

Yes: it's an IP threat feed your firewall downloads on a schedule. Each vendor has its own name for it: External Dynamic List on Palo Alto, threat feed on FortiGate, IoC feed on Check Point, Security Intelligence feed on Cisco, dynamic address feed on Juniper, third-party threat feed on Sophos, feed list on F5, URL Table alias on pfSense and OPNsense.

Do I need to install anything?

No. Your firewall pulls the list over HTTPS. You can also use blocklists with the free CrowdSec Security Engine if you want behaviour detection on your servers too.

How often are the lists updated?

Several times a day. Devices pull every hour on paid plans, every 24 hours on the free plan.

Will a blocklist block legitimate traffic?

Lists curated by CrowdSec are built to have zero false positives; legitimate services are excluded automatically. Third-party lists we republish are cleaned but not guaranteed.

Can I get lists targeting my industry or country?

Yes: there are lists of IPs attacking banks, healthcare, retail, public sector and more, and lists by targeted country.

What's free and what's paid?

The free plan includes three lists. Paid plans remove the limit and add premium and Platinum lists (see pricing).

Resources

Le Monde Uses CrowdSec to Automate Protection of Internet-Facing Resources and Maximize Operational Efficiency
SUCCESS STORY

Le Monde Uses CrowdSec to Automate Protection of Internet-Facing Resources and Maximize Operational Efficiency

Read more
Leveraging Blocklists for Optimized Protection
ACADEMY COURSE

Leveraging Blocklists for Optimized Protection

Get free course
The Real Value of Preemptively Blocking a Cyber Attack
BLOG

The Real Value of Preemptively Blocking a Cyber Attack

Read more