How to prioritise CVEs by real exploitation, beyond CVSS, EPSS and KEV
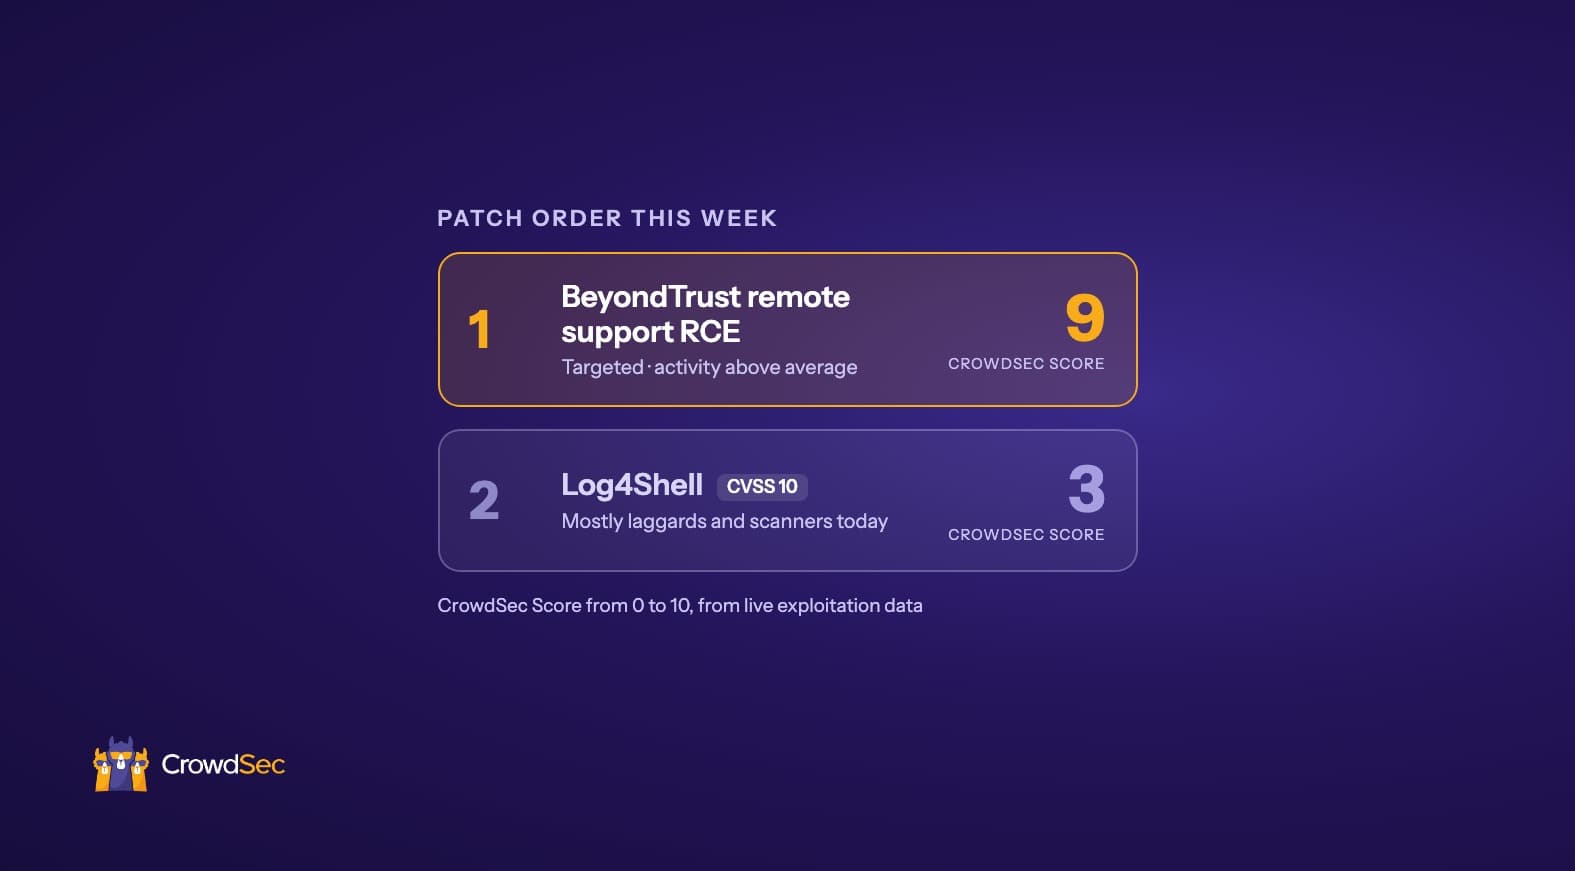
CVSS, EPSS and KEV estimate risk. To prioritise patching, check if a CVE is exploited now, how targeted it is and whether it’s growing. A practical method.
Tutorial
PHP2Shell Virtual Patching: Keep Your PHP Websites Online While You Upgrade
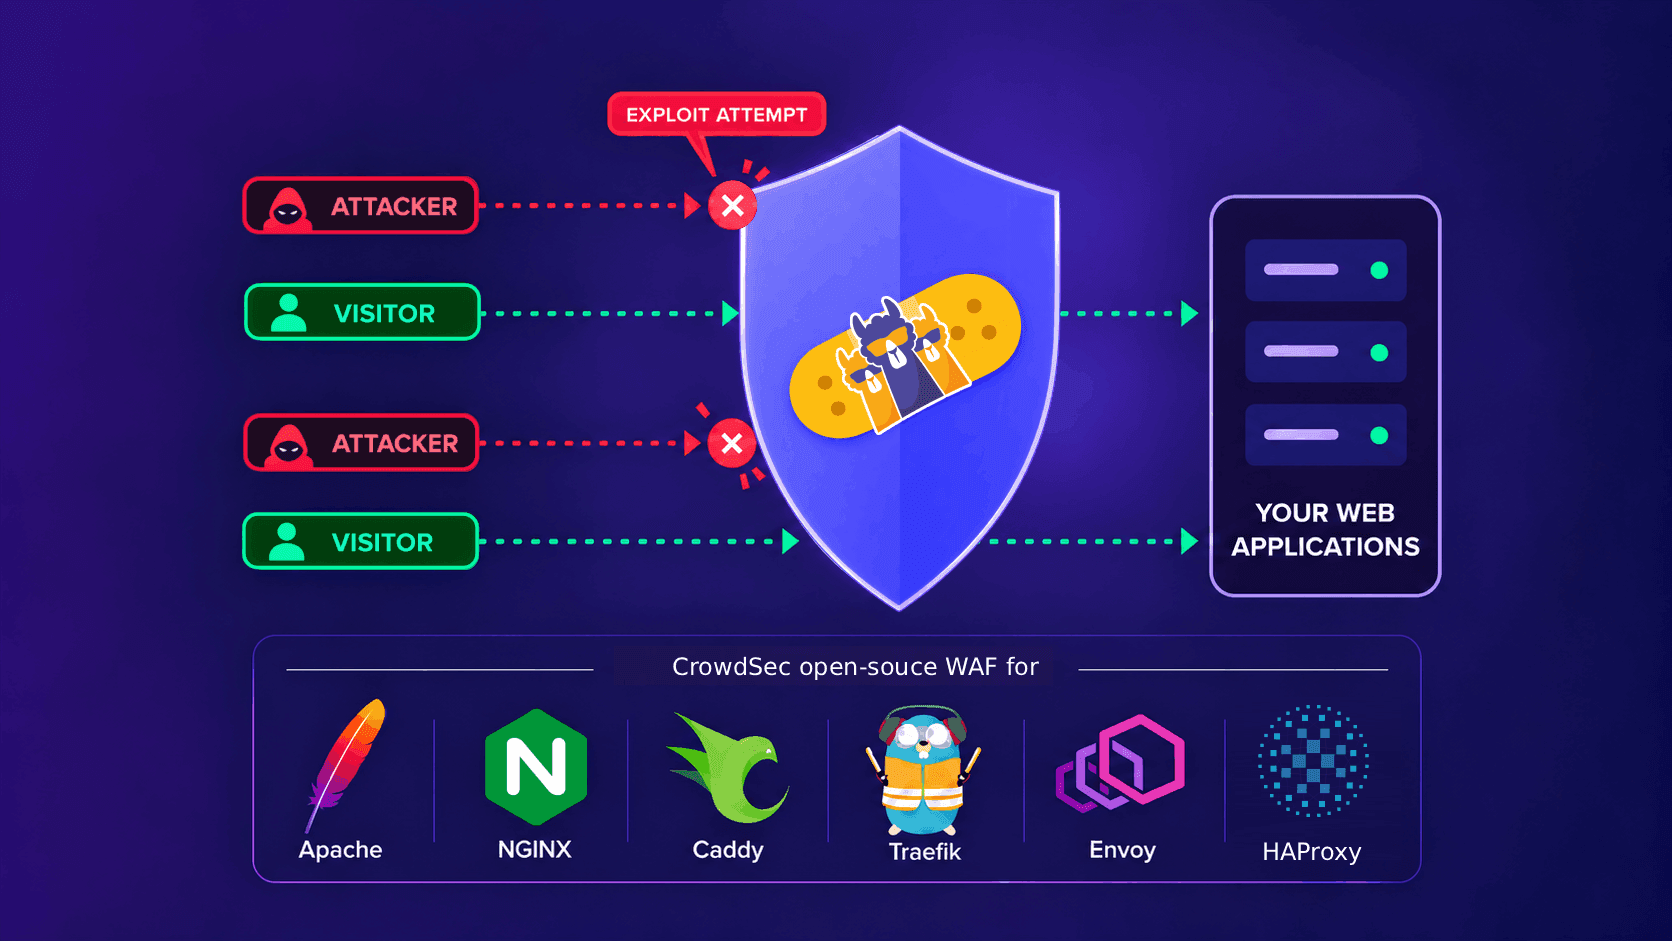
PHP2Shell virtual patching: free CrowdSec WAF rules block known exploits for both CVEs, so your PHP sites stay online while you upgrade. How to set it up.
Proactive Cybersecurity
What 300,000 Security Engines saw: 8 lessons on exploitation from SANS 2026
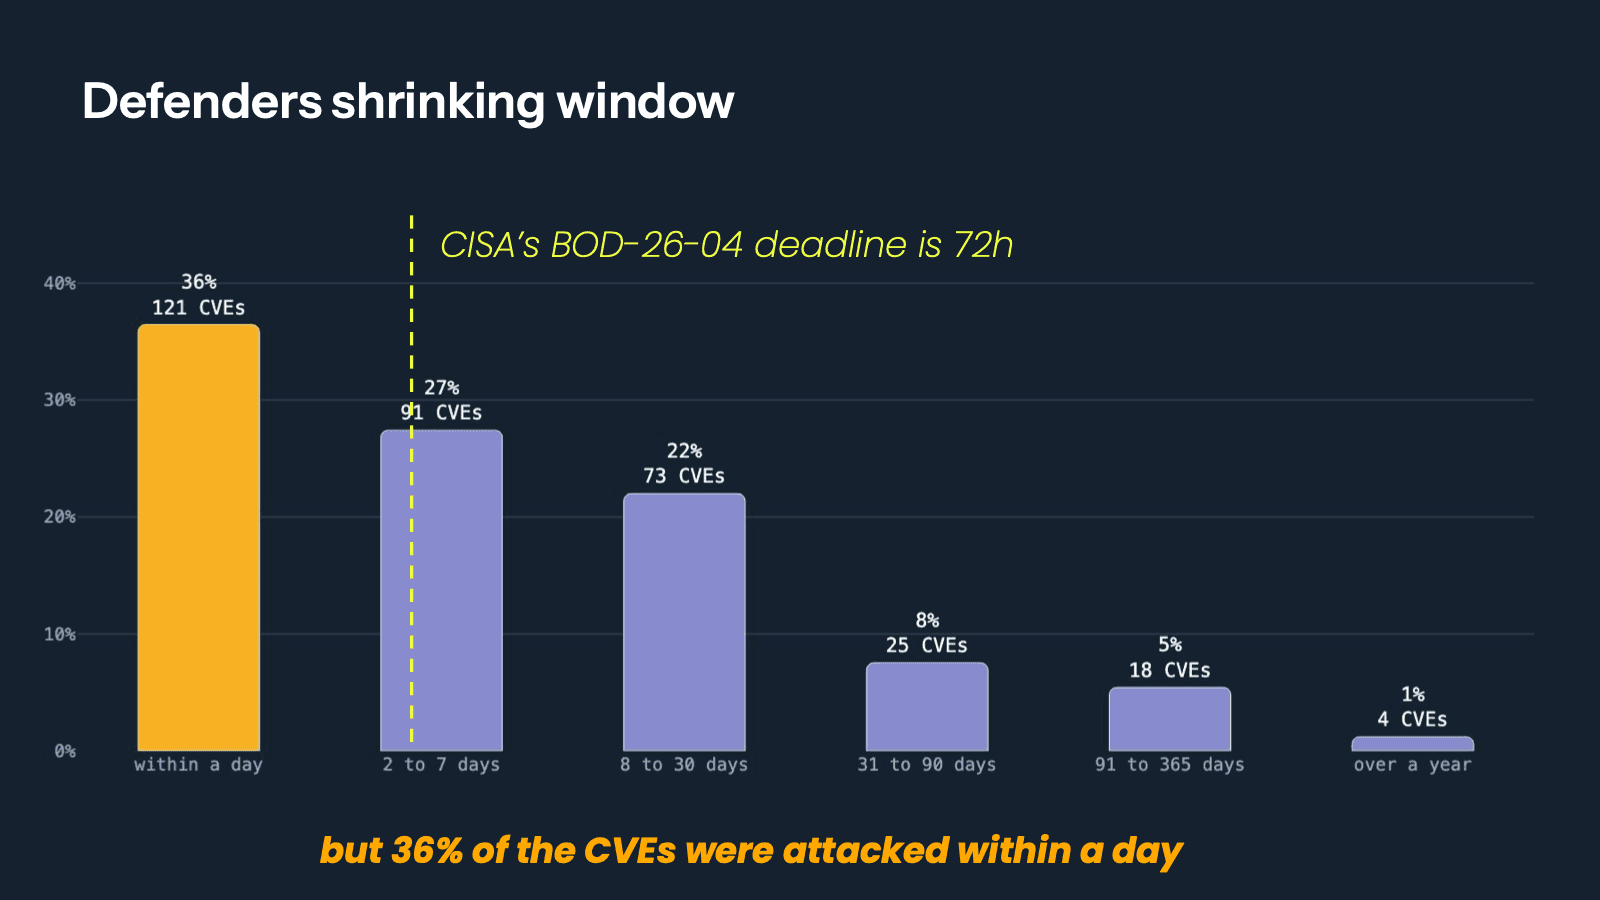
36% of exploited CVEs were attacked within a day of publication. What 300,000 Security Engines saw at SANS 2026: borrowed cloud IPs, early zero-days, old CVEs.