Download the latest Vulnerability & Exploitation Report

Download now
Blog

Thought Leadership

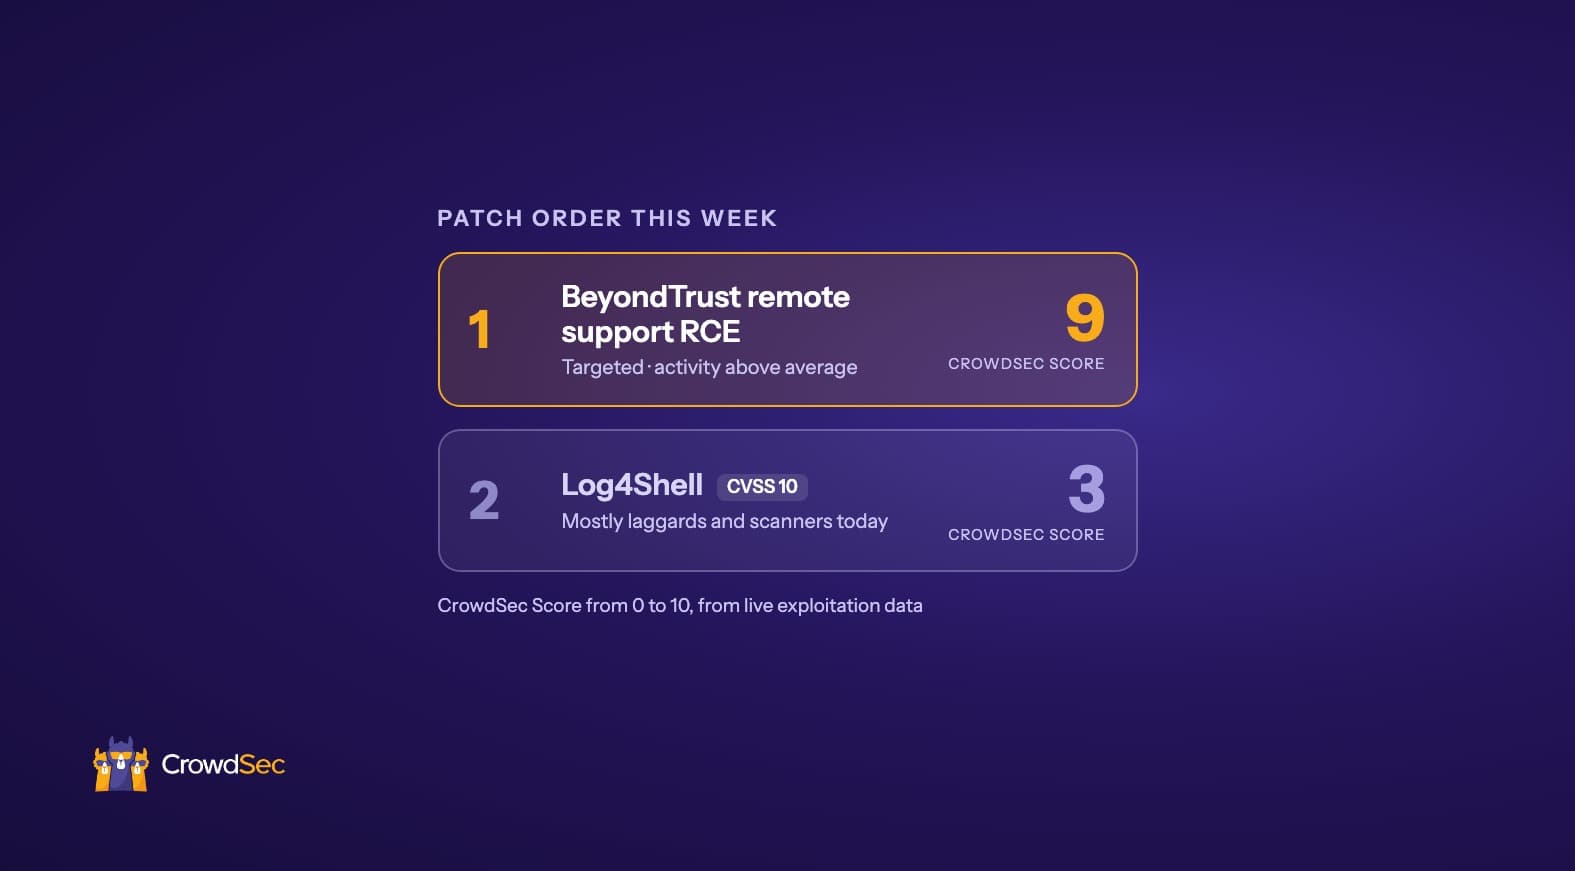
Patch order example: the BeyondTrust remote support RCE ranks first with a CrowdSec Score of 9, ahead of Log4Shell, which has a CVSS of 10 but a CrowdSec Score of 3.
Proactive Cybersecurity

How to prioritise CVEs by real exploitation, beyond CVSS, EPSS and KEV

CVSS, EPSS and KEV estimate risk. To prioritise patching, check if a CVE is exploited now, how targeted it is and whether it’s growing. A practical method.

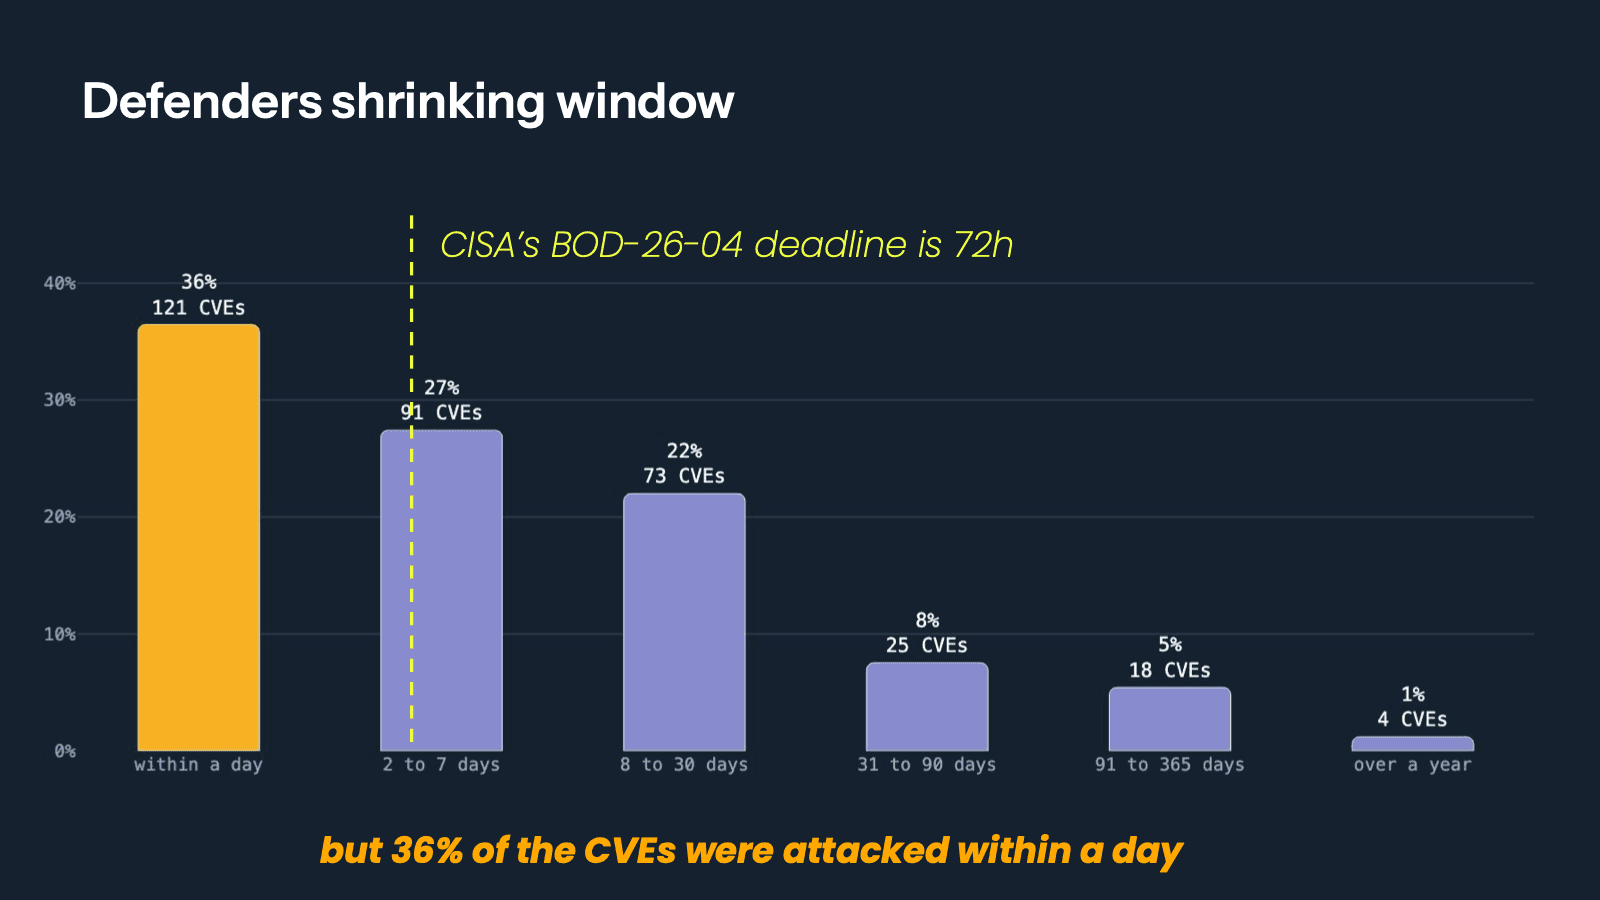
Bar chart: of 332 exploited CVEs tracked from Q4 2024 to Q2 2026, 36% were attacked within a day of publication, 27% within 2 to 7 days and 22% within 8 to 30 days
Proactive Cybersecurity

What 300,000 Security Engines saw: 8 lessons on exploitation from SANS 2026

36% of exploited CVEs were attacked within a day of publication. What 300,000 Security Engines saw at SANS 2026: borrowed cloud IPs, early zero-days, old CVEs.

Illustration comparing a single IP reputation lookup with a full cyber threat intelligence investigation
Proactive Cybersecurity

IP reputation vs full CTI: what your SOC actually needs

Most SOCs need fast IP reputation in their SIEM before they need attribution-heavy CTI. How to tell them apart, and what to ask any IP reputation vendor.

Is AI digital inbreeding 2.0?
Thought Leadership

Is AI digital inbreeding 2.0?

Artificial Intelligence is making its breakthrough into society, fed mainly by a western-thinking subgroup of mankind. The question arises – what kind of impact will this have on our lives? Will it be an exceptional advantage or snowball into a kind of inbreeding 2.0 similar to what we saw with the Royals and regimes of the past? Philippe Humeau shares his take on this topic.