Know which CVEs are exploited right now, and block the attackers
CVSS, EPSS and KEV estimate risk. The Live Exploit Tracker shows what attackers are actually doing: which CVEs are exploited right now, whether attacks are targeted or mass scanning, whether activity is surging or fading, and which IPs are behind them. Its reconnaissance rules go further back: they show which technologies attackers are probing before a CVE is even published in the NVD, a pre-NVD warning most vulnerability feeds can't give. Subscribe your firewall to a CVE or to a whole vendor and block exploiters while you patch.
- Real-world Exploit Telemetry
- Block Malicious IPs in Real Time
- Prioritize CVEs by Active Exploitation

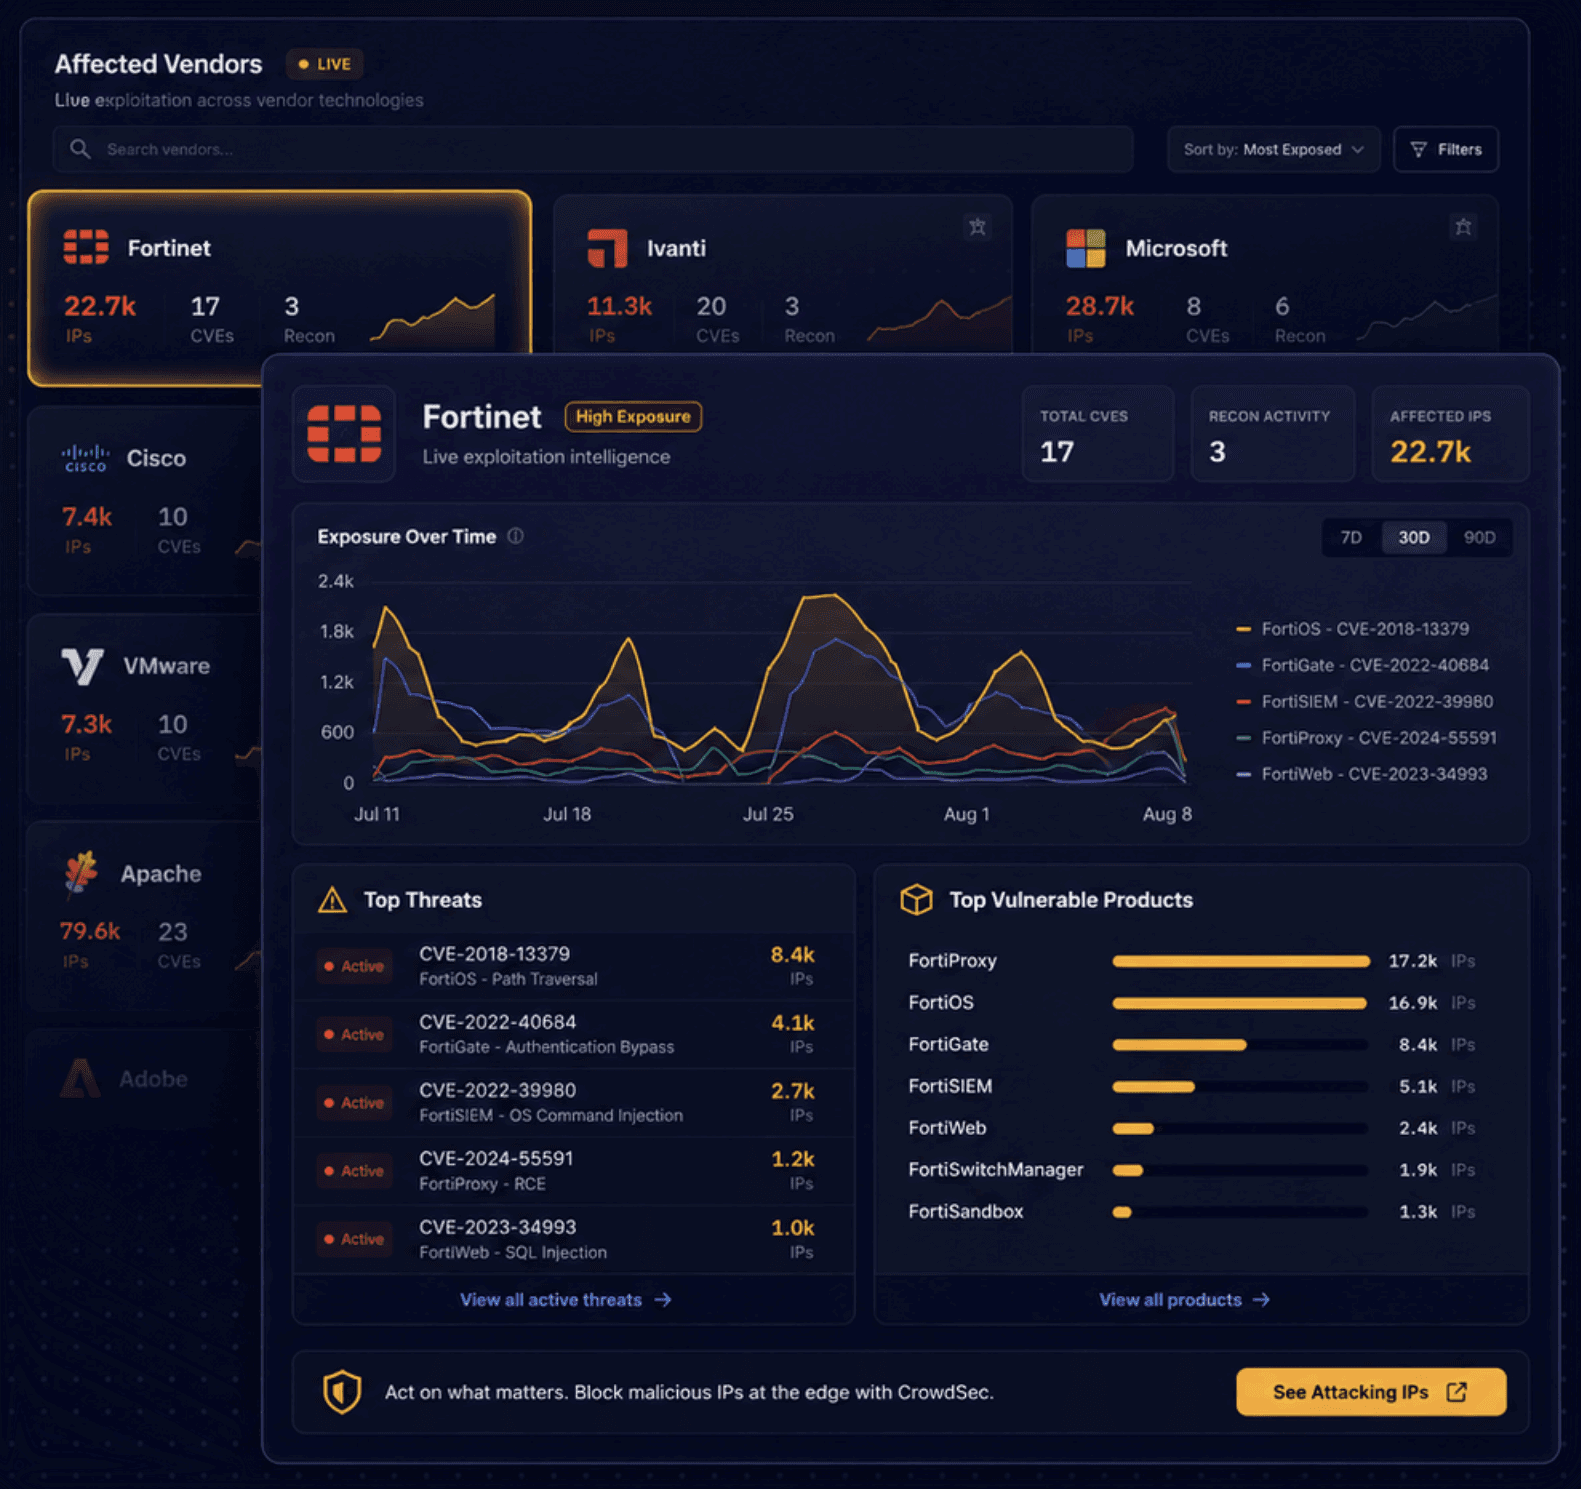

Gain Accurate Visibility into What’s Actively Being Exploited in the Wild
Live Exploit Tracker delivers observational, ground-truth intelligence based on live attacks seen across hundreds of thousands of production systems worldwide.
KEV, CVSS and EPSS scores estimate likelihood. Live Exploit Tracker shows reality.
Preemptively block attackers
Get a continuously updated list of IPs actively exploiting a given CVE, usable as a raw TI feed or as an edge-consumable blocklist format.
Prioritize What Actually Matters
Few CVEs are actual emergencies, but they are deadly. The Live Exploit Tracker reports real-world exploitation, enabling you to triage and patch vulnerabilities that are currently exploited in the wild.
Detect Accurately
Our IOCs are observed at scale in the wild, allowing you to create accurate detection rules based on real-life attacks, not hallucinated or dysfunctional exploits.

Data that actually helps you
700+
Actively exploited CVEs
100+
Vendors
250K+
CrowdSourced Machines
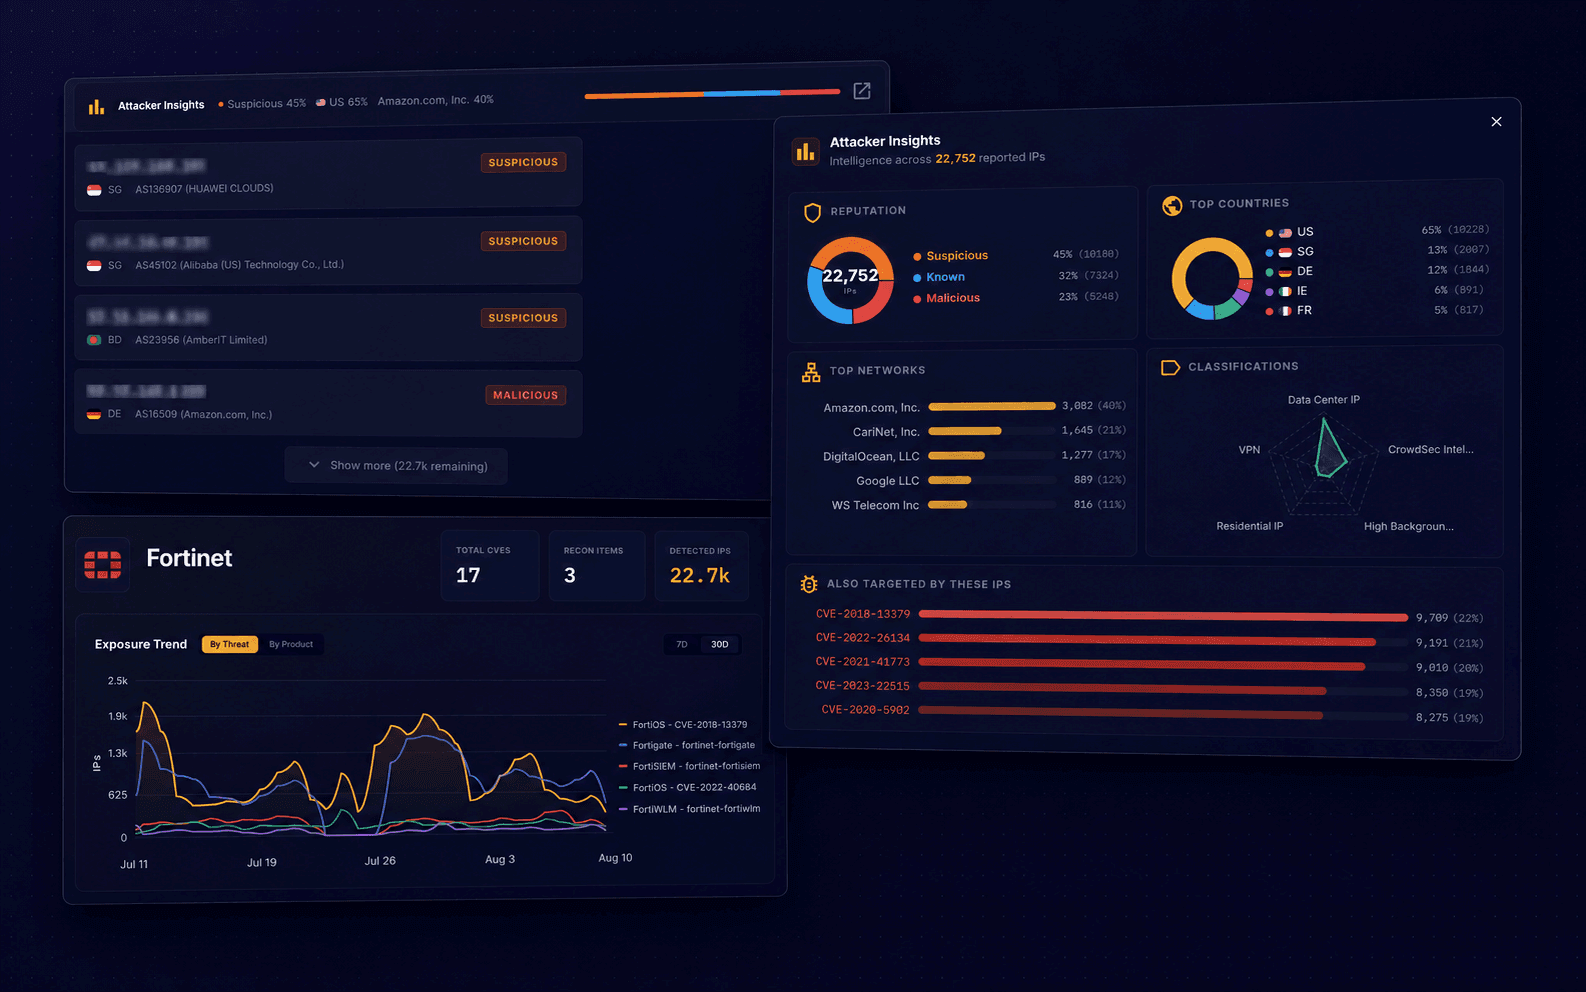
Don’t track individual vulnerabilities, protect your stack
We go beyond vulnerabilities: We let you protect a specific vendor or product in your stack. Cover not only vulnerabilities but also pre-attack reconnaissance.
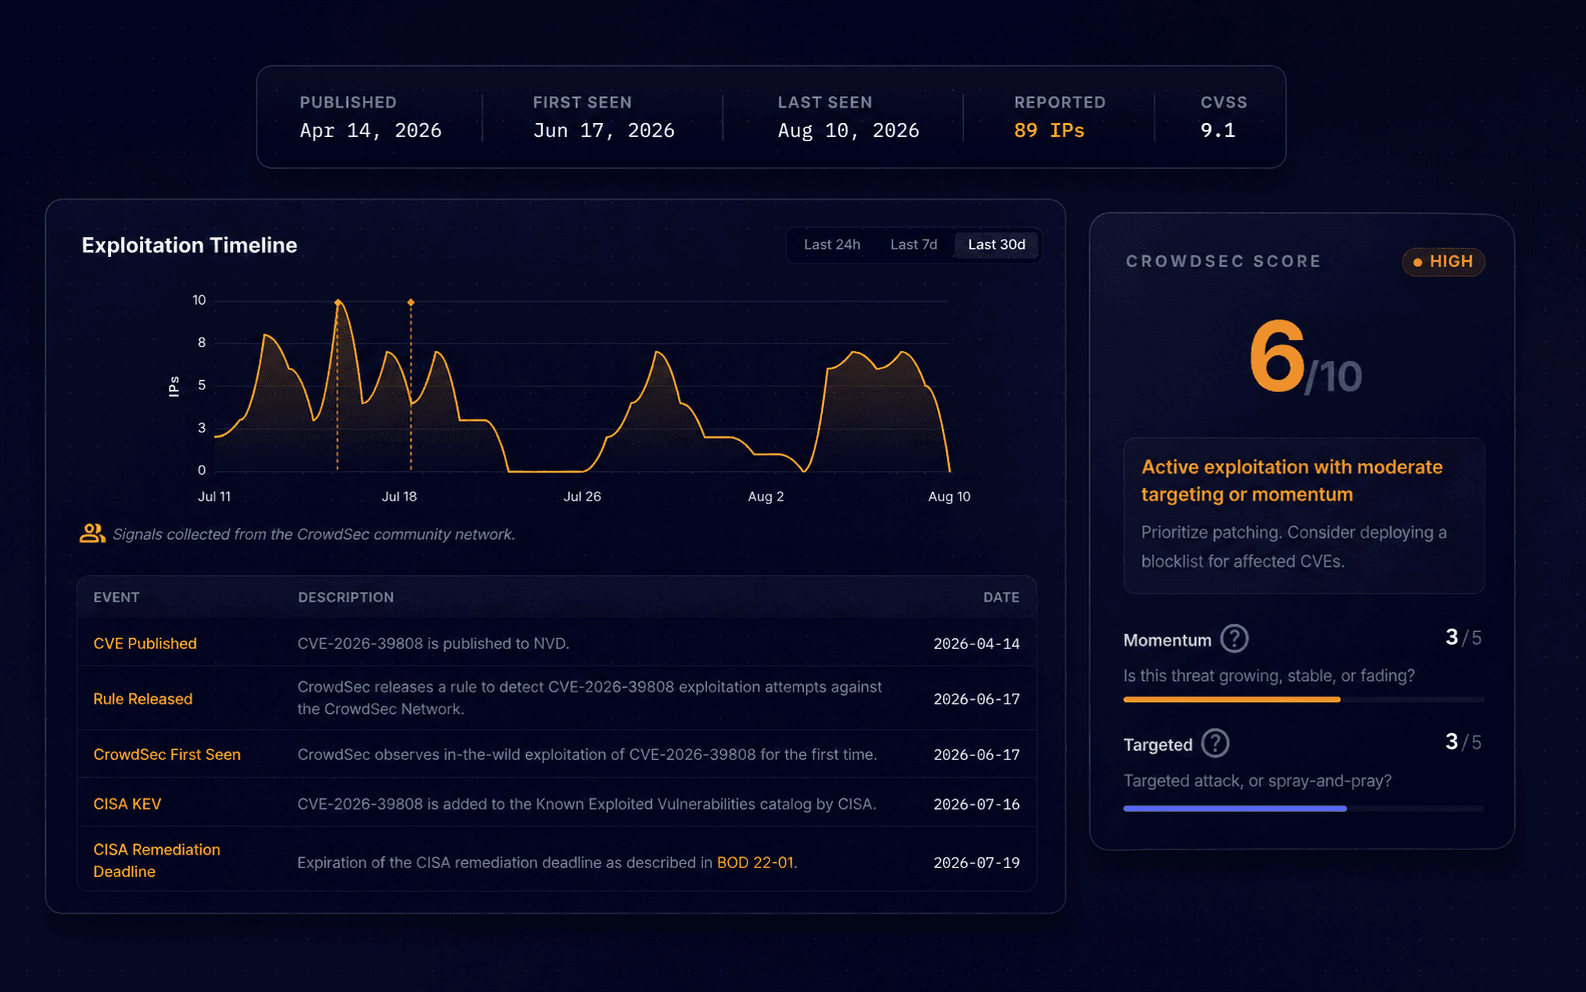
Vulnerabilities aren’t static. Neither should you be.
Vulnerabilities are going through cycles, exploitation momentum, and attackers’ behaviour knowledge let you prioritise your actions.
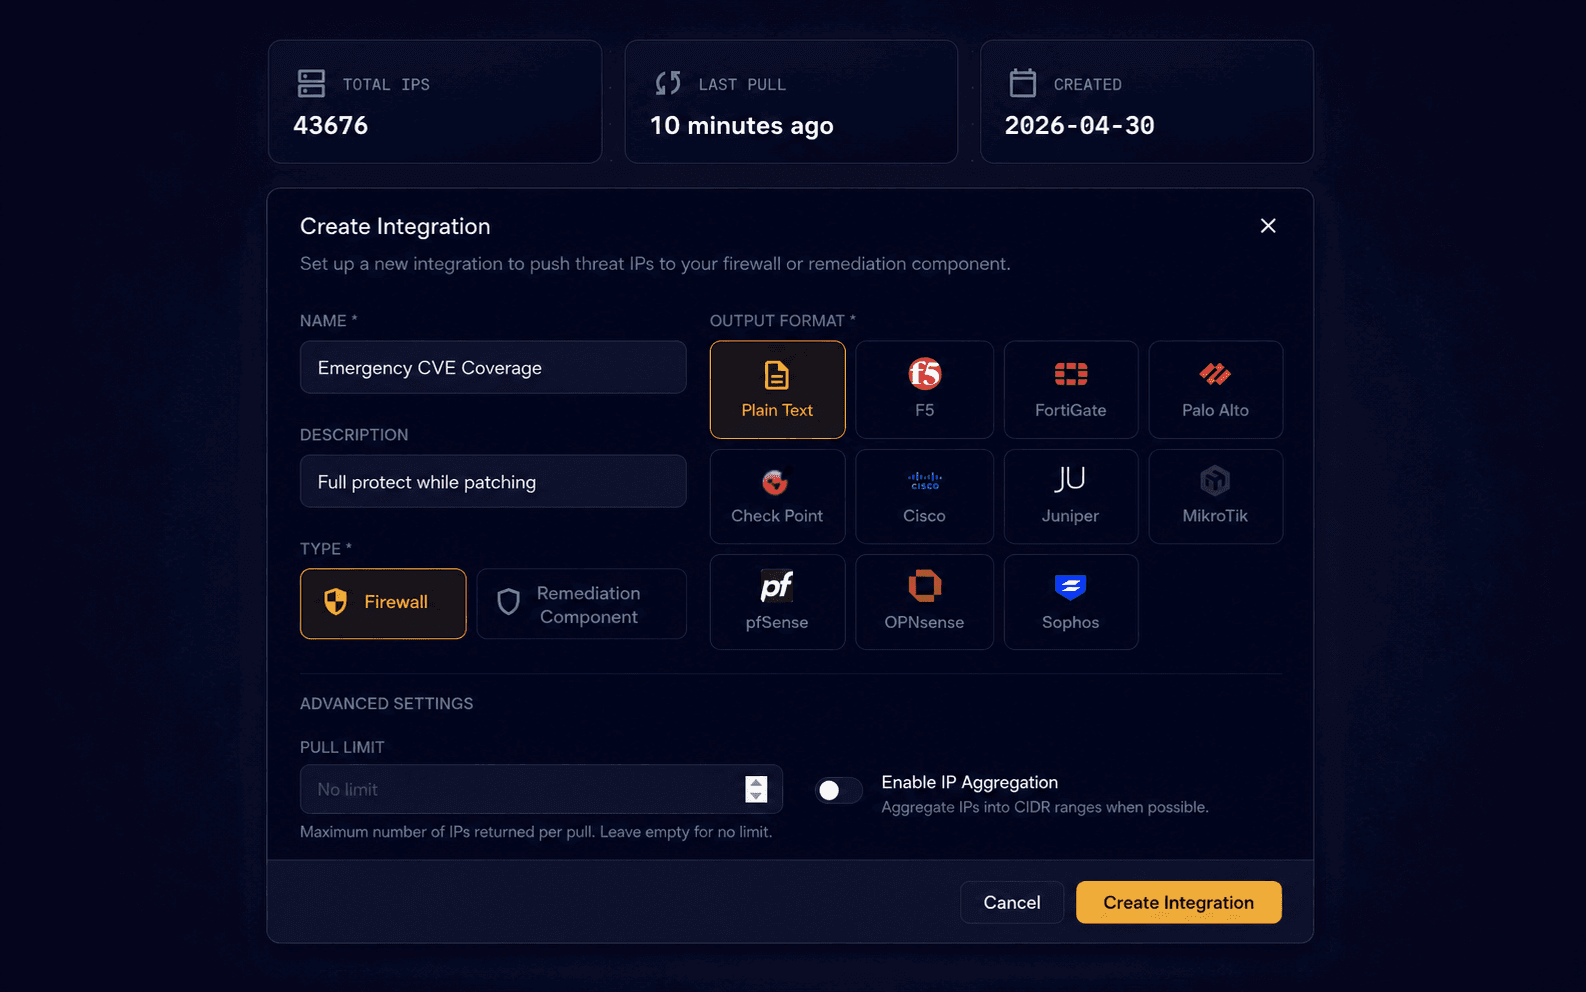
Leverage your existing stack
Inject our blocklists into any existing equipment or software, including CDN, hardware firewall, cloud provider, Virtual Machine, or Container. Deploy in minutes and see results in hours.

Key Features & Capabilities
Live Exploit Tracker Score
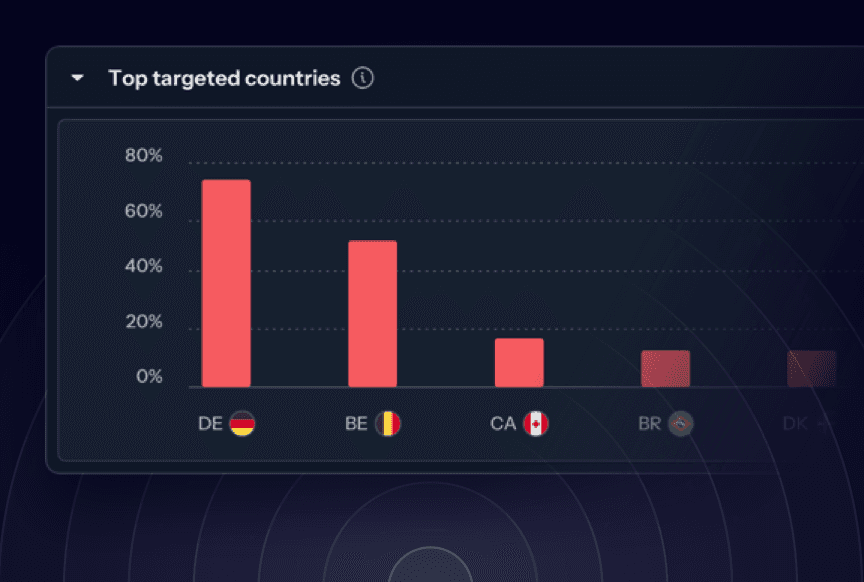
A composite score built from observed exploitation factors like profile (opportunistic → targeted), scale, timeline, and intensity, plus top targeted countries per vulnerability.
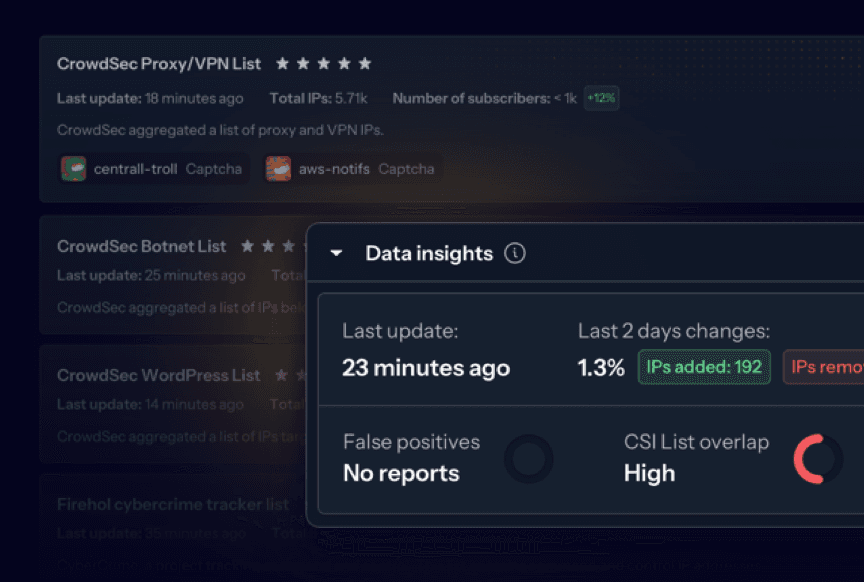
Exploit IP Feed (per CVE)
A continuously updated list of IPs exploiting a specific CVE, refreshed multiple times per hour, with IPs added/removed based on recent activity.
Pre-CVE Scouting
List of IPs probing a vendor/technology over the last ~36h, including campaigns hunting for “unknown CVEs.”
Top Targeted Countries
Understand geographic targeting trends per vulnerability to improve threat modeling, align defenses with attacker focus, and support geopolitical risk assessments.
Frequently asked questions
How do I know if a CVE is actively exploited?
How is the CrowdSec Score different from CVSS, EPSS or KEV?
Can I block the IPs exploiting a specific CVE?
What does pre-NVD mean?
What are reconnaissance rules?
How do I get access?
Ready to Cut Through the CVE Chaos?
Contact our sales team to unlock all the features: IoCs, IP lists, and more.
Explore the CrowdSec Products
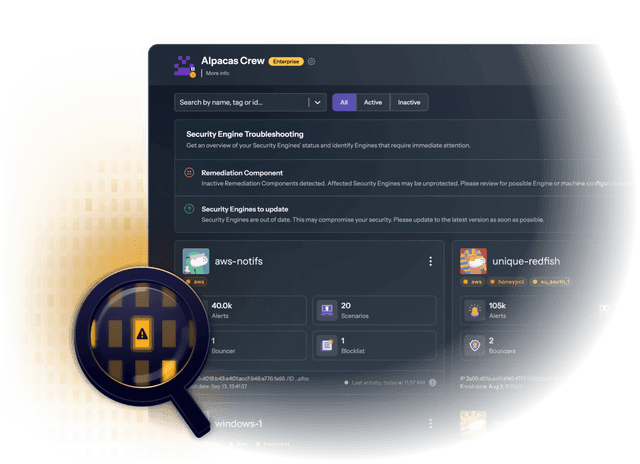
Security Stack
CrowdSec’s behavioral solution against targeted attacks consists of the Console, Security Engine, Remediation, and AppSec Components. Adapt and configure the CrowdSec Security Stack to fit your IDPS or WAF needs.
Get started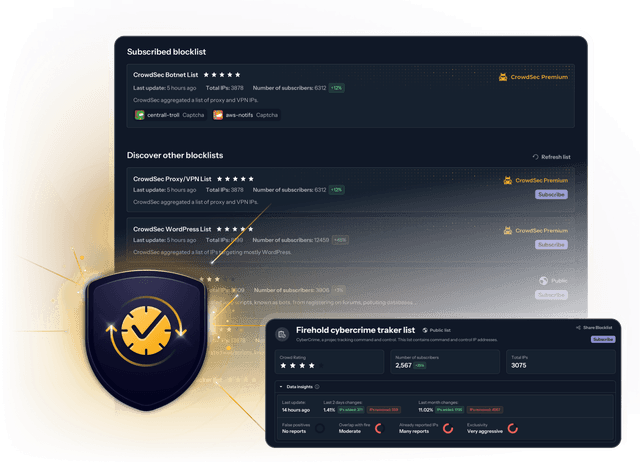
Blocklists
Block mass exploitation attempts before they reach your perimeter and get immediate protection against active malicious IPs with CrowdSec’s ultra-curated, actionable, and real-time blocklists.
Get started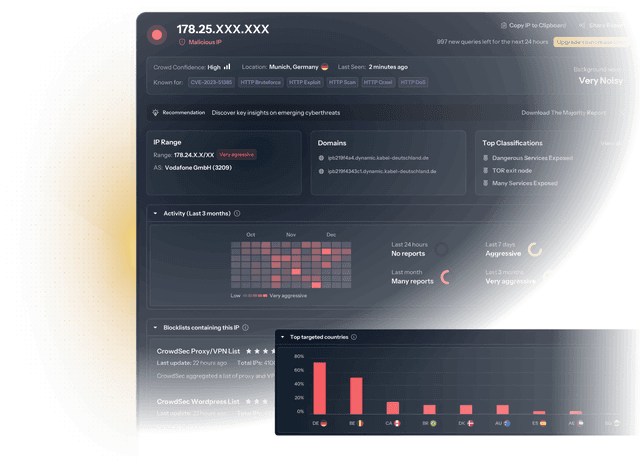
CTI
Access the most advanced real-world CTI distributing IP reputation intelligence that helps you detect, investigate, and respond to cyber threats more effectively and efficiently.
Try for free