CrowdSecApplication Security
Enhance Your Application Security with CrowdSec's Web Application Firewall
Protect web applications with virtual patching, OWASP CRS, behavioral detection, bot protection, and CrowdSec's crowdsourced threat intelligence — all powered by the CrowdSec Security Engine.
WAF is a Crucial Component of YourApplication Security Strategy
Protect against web-based attacks
Protect web applications by filtering and inspecting incoming traffic and applying application-layer security controls.
Reduce exploitation risk
Use targeted virtual patches and broader OWASP CRS coverage to reduce exposure to known and newly disclosed vulnerabilities.
Detect more than individual malicious requests
Combine request inspection, behavioral detection, bot protection, and CrowdSec threat intelligence to identify malicious activity and attack patterns.
CrowdSec WAF
Advanced Application Security Needs an Advanced WAF Solution.
Modern web threats cannot always be stopped by inspecting a single request against a generic rule set. CrowdSec adds multiple application-security layers to the Security Engine, allowing you to combine precise vulnerability protection, broad WAF coverage, behavioral detection, bot mitigation, and crowdsourced intelligence.
Start now
Low-Effort Virtual Patching
Apply targeted protections for specific vulnerabilities, including newly disclosed and actively exploited CVEs. CrowdSec virtual patches complement broader WAF rules with narrowly scoped detection logic, helping reduce exposure while an upstream patch or remediation is being deployed.
OWASP CRS Coverage
Use the OWASP Core Rule Set for broad protection against common classes of web attacks, including techniques such as SQL injection, cross-site scripting, and local file inclusion. Combine CRS coverage with CrowdSec's more targeted virtual patches according to your application's risk profile.
Advanced Behavior Detection
Go beyond isolated request inspection. CrowdSec can correlate events across multiple requests to identify malicious behaviors and attack patterns that traditional request-by-request WAF rules may miss.
Bot Detection and Mitigation
Detect sophisticated automated traffic using signals and challenge mechanisms designed to distinguish automated clients from legitimate browser activity. CrowdSec's bot-protection capabilities can help address scraping, scalping, aggressive automation, and distributed bot activity while allowing legitimate bots and environment-specific exceptions to be handled separately.
Crowdsourced Threat Intelligence and Blocklists
Application protection does not have to begin only when a malicious request reaches the WAF. CrowdSec's community-powered threat intelligence and curated blocklists can help identify known malicious infrastructure and apply security decisions earlier in the defensive chain.
Granular Protection — Not a Black Box
Choose the protection layers and rules that fit your environment. CrowdSec gives operators visibility and control over detection logic, allowing protections to be inspected, enabled, disabled, tuned, or extended with custom scenarios and patterns where needed.
Start with narrowly targeted virtual patches and progressively add broader CRS coverage, behavioral detection, bot mitigation, and blocklists according to the application's risk profile.
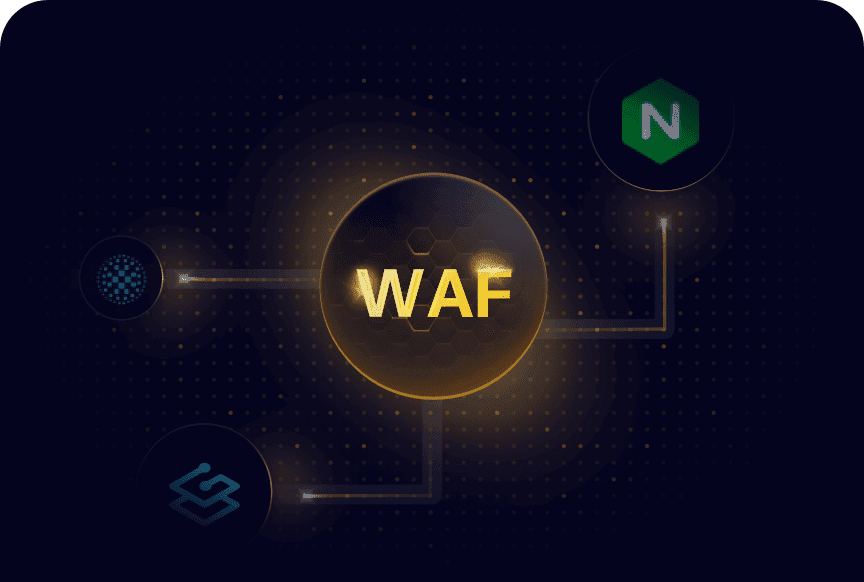
Designed for Existing Web Infrastructure
Deploy CrowdSec application-security capabilities through supported integrations with web servers, reverse proxies, and Remediation Components, without requiring you to replace your existing web infrastructure.
Feature availability can vary by integration. Refer to the current CrowdSec documentation for compatibility details, particularly for newer capabilities such as bot detection.
Powered by the CrowdSec Security Engine
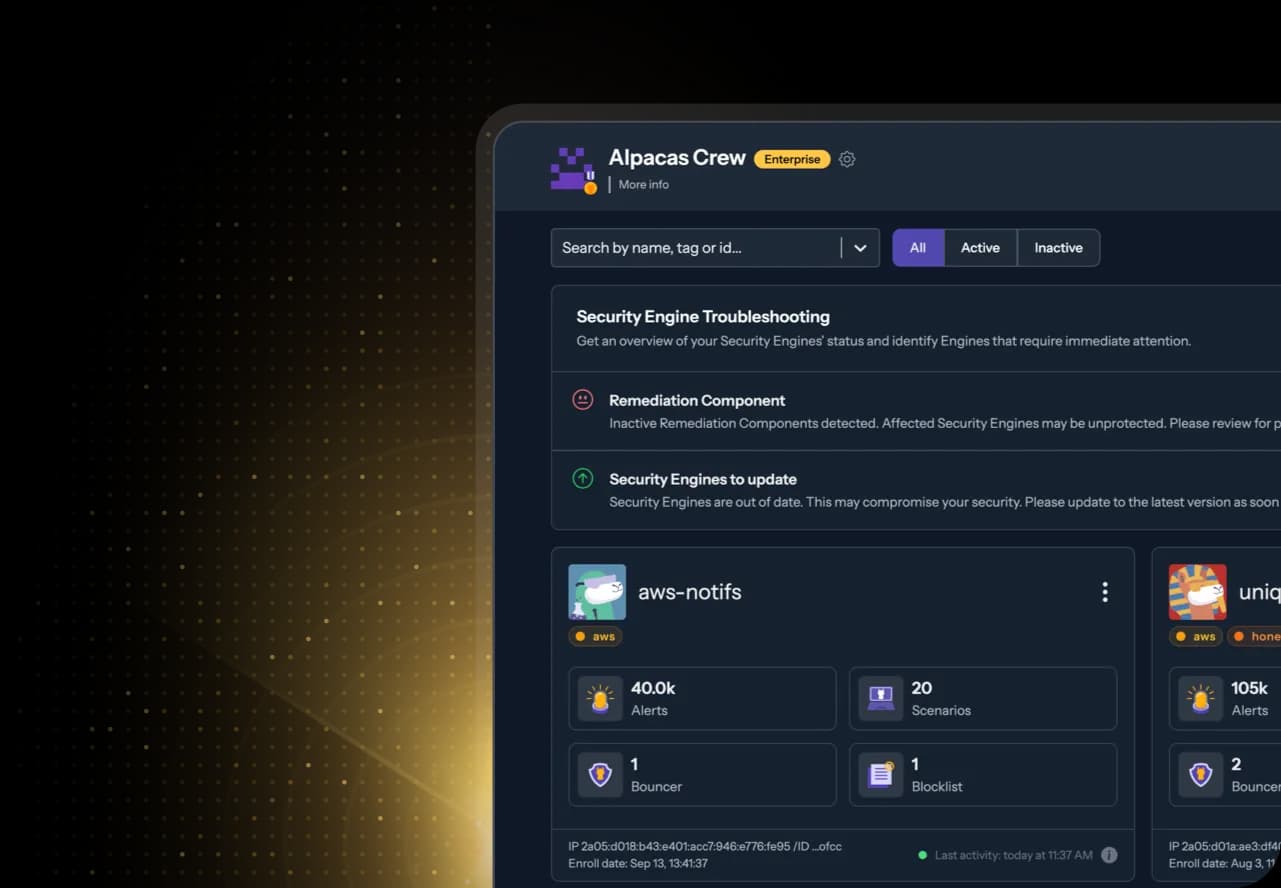
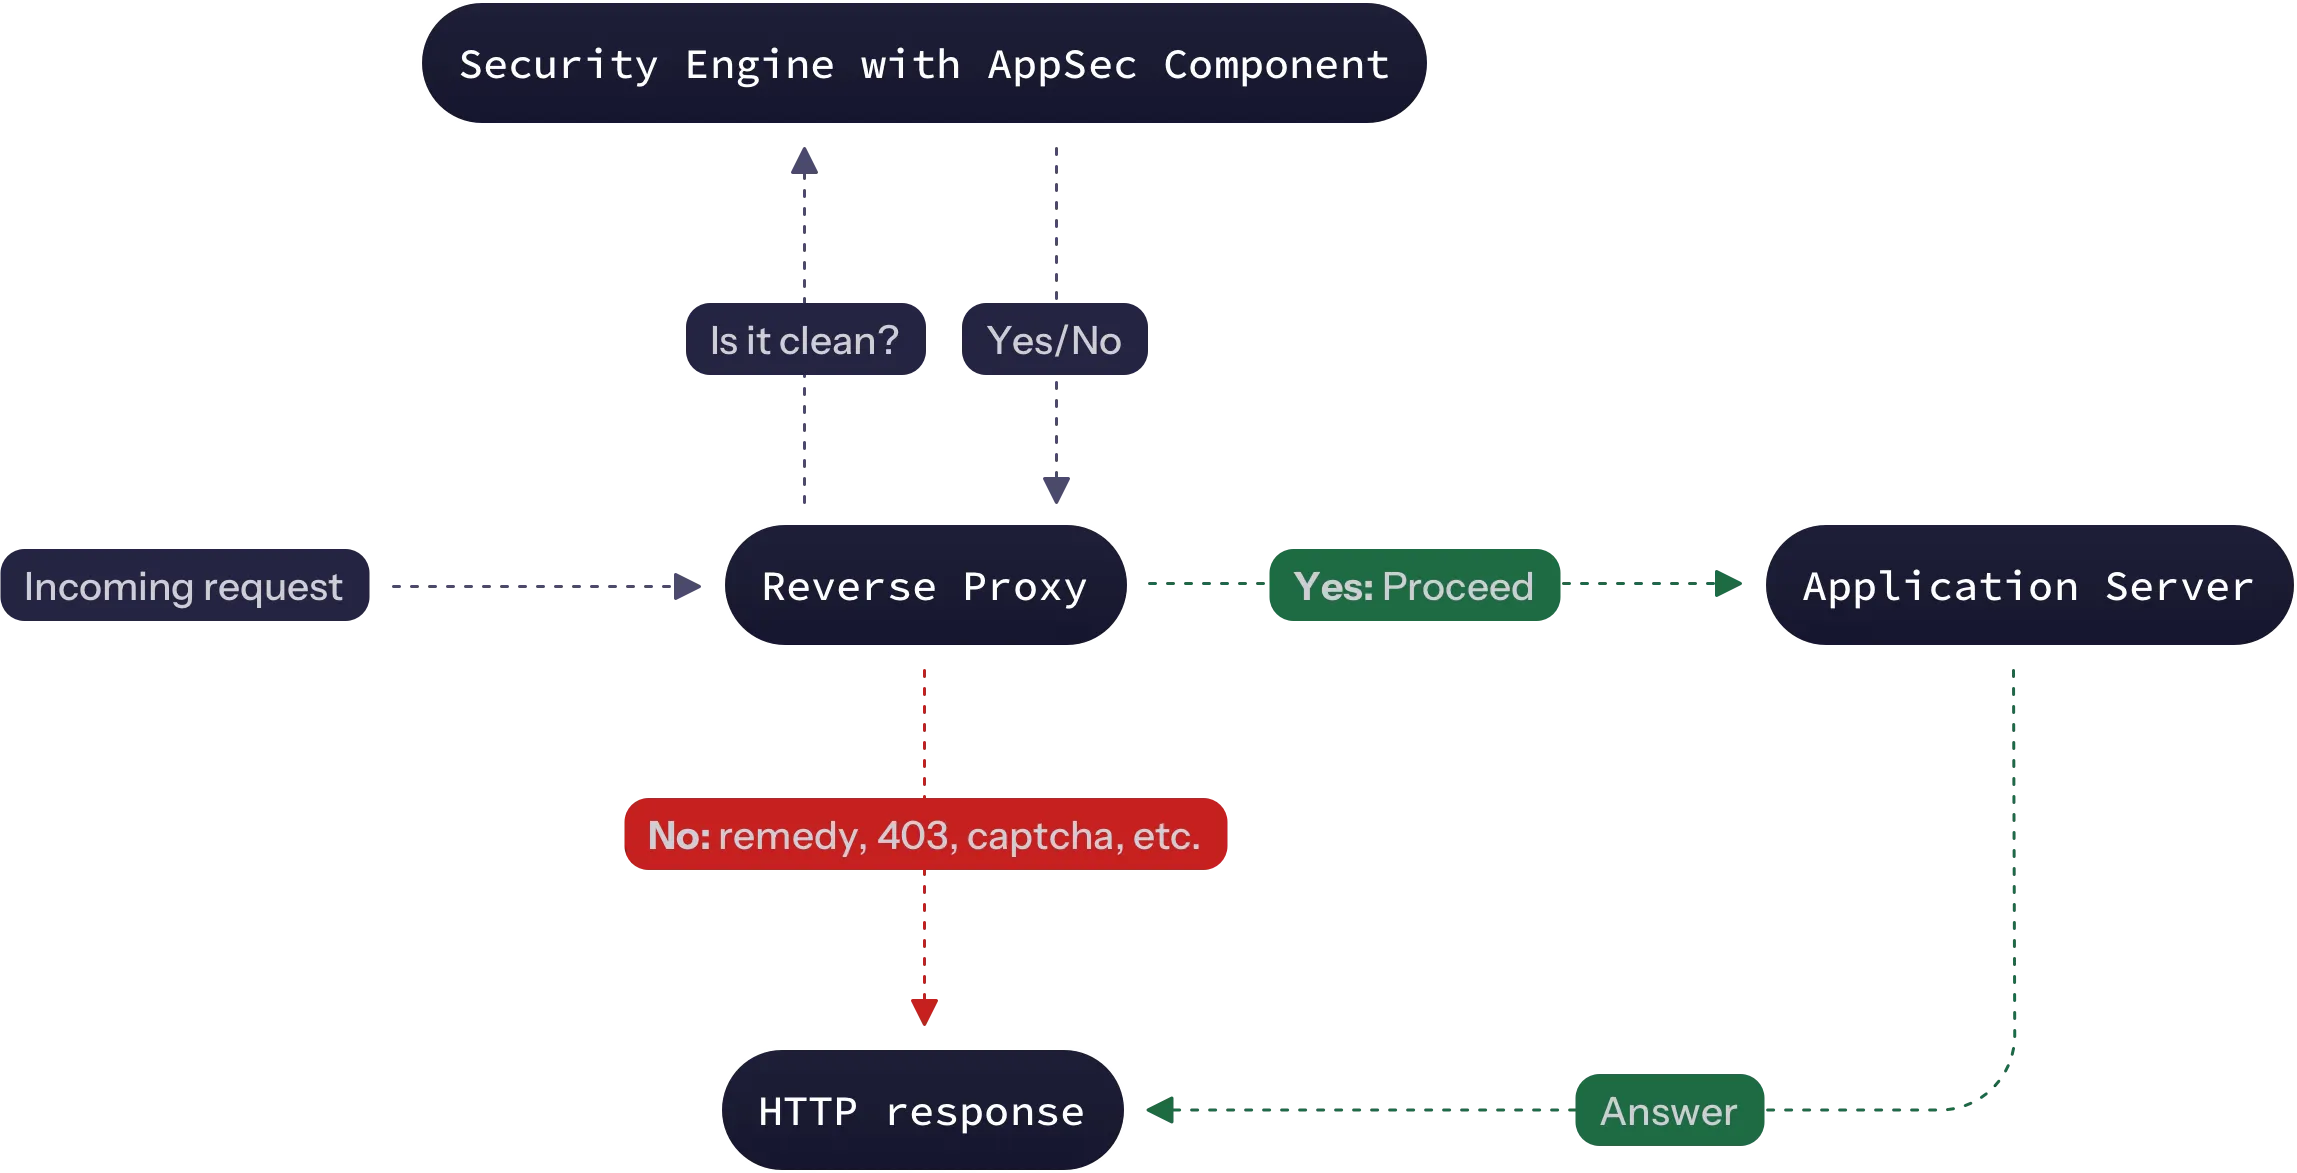
CrowdSec's application-security capabilities extend the Security Engine to analyze web traffic and generate security decisions. Remediation Components integrate with supported web servers and proxies to enforce those decisions, while the CrowdSec Console provides visibility and management across the deployment.
Get Started with CrowdSec Application Security
Choose a supported Remediation Component, install the CrowdSec Security Engine, and activate the application-security capabilities needed for your environment.
1
Sign up to the CrowdSec ConsoleGet Started
2
Install the Security Engine
3
Install the appropriate Remediation Component
4
Activate and configure the AppSec Component
Explore the CrowdSec Security Stack