CrowdSec Welcomes db.gcve.eu, Strengthening Europe’s Vulnerability Intelligence, Without Losing Global Interoperability
A healthier vulnerability ecosystem is open, federated, and resilient.
At CrowdSec, we’re excited about the public launch of db.gcve.eu, a new open vulnerability advisory database built to aggregate, normalize, and correlate vulnerability information across multiple publishers while remaining compatible with existing CVE workflows.
What is db.gcve.eu?
db.gcve.eu provides a unified view of vulnerabilities by continuously collecting and correlating advisories from a wide range of public sources, including 25+ sources for now.
Under the hood, it is powered by Vulnerability-Lookup, an open source project aligned with GCVE’s best current practices for collection and publication. It also ships with open access, a public API, and data dumps for bulk/offline use. It is precisely what defenders need to build automated workflows and repeatable processes.
Why this matters for European defenders
Security teams don’t just need more data. They need trusted, sovereign, and resilient access to it.
db.gcve.eu is hosted and operated by CIRCL in Luxembourg, and the project is co-funded by CIRCL and the European Union (ECCC) under the FETTA project. That combination of open-source and European-operated infrastructure is a meaningful step for digital sovereignty and operational continuity.
Just as importantly, this is not about “replacing” the global ecosystem. It’s about strengthening it.
Why “multiple sources” wins in vulnerability intelligence
Anyone running vuln management at scale knows the pain:
- One source updates first, another lags
- One vendor advisory has the best technical detail
- Another database has the best cross-references
- Exploit and “known exploited” assertions show up in different places
db.gcve.eu’s value is in doing the unglamorous but essential work: aggregation, correlation, and normalization across identifiers and databases, so defenders can spend less time reconciling records and more time acting.
This “multi-source first” stance is not a luxury. It’s how you reduce blind spots.
Real-time attacker reality, grounded in production
Vulnerability databases increasingly do more than list “what could be exploited.” Initiatives like GCVE / db.gcve.eu also incorporate community feedback and exploitation signals (including from major public telemetry providers such as Shadowserver) to help validate what’s happening in the wild.
That’s exactly the direction the ecosystem should go, and it’s where CrowdSec adds a different kind of signal: high-fidelity production telemetry.
Where many “exploitation proofs” come from honeypots, CrowdSec’s Live Exploit Tracker is built on real attacks seen across real production systems.
That’s where CrowdSec naturally connects db.gcve.eu’s enriched advisory view with CrowdSec’s Live Exploit Tracker, which focuses on:
- CVEs actually observed being exploited in operational environments
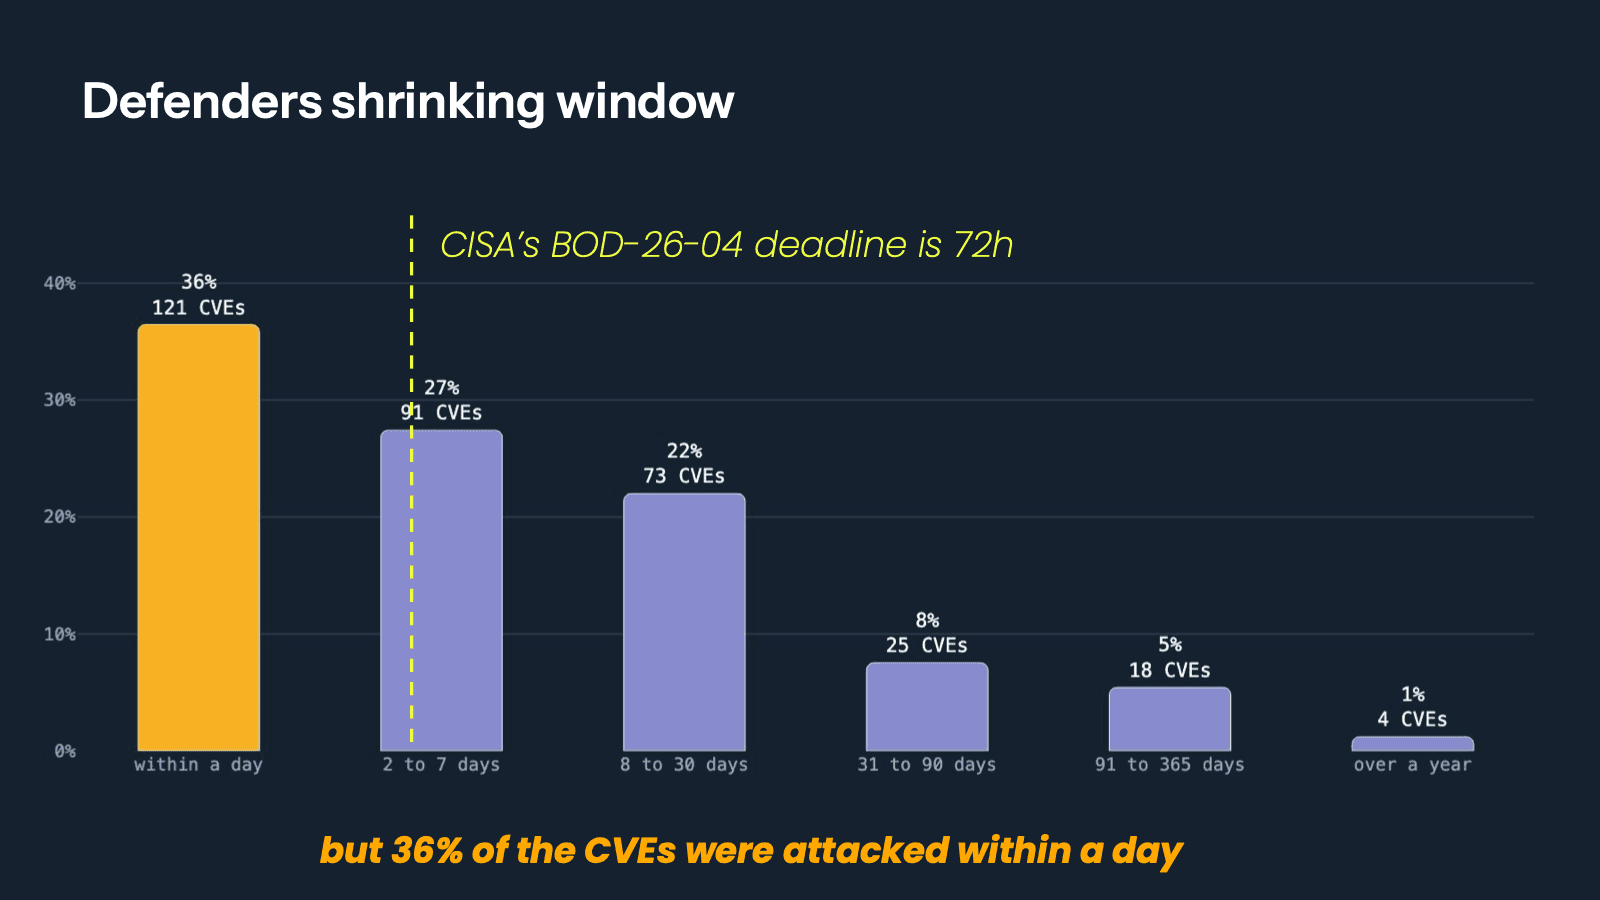
- Time-to-exploitation and ongoing exploitation trends as they unfold
- Concrete attacker information (IPs, IoCs, exploitation behavior), usable for rapid mitigation and threat hunting
Put simply:
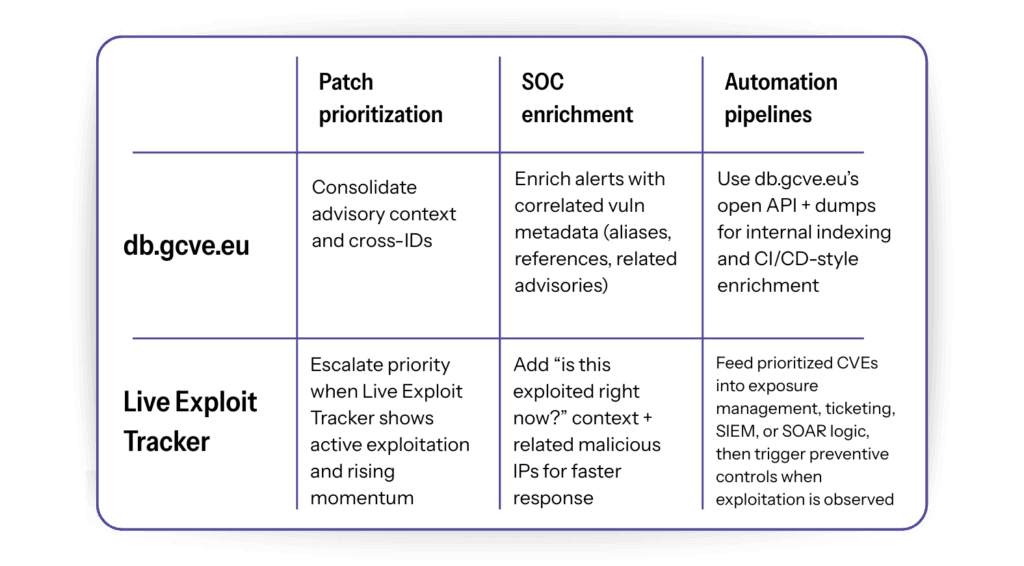
- db.gcve.eu helps you correlate and contextualize vulnerabilities across sources.
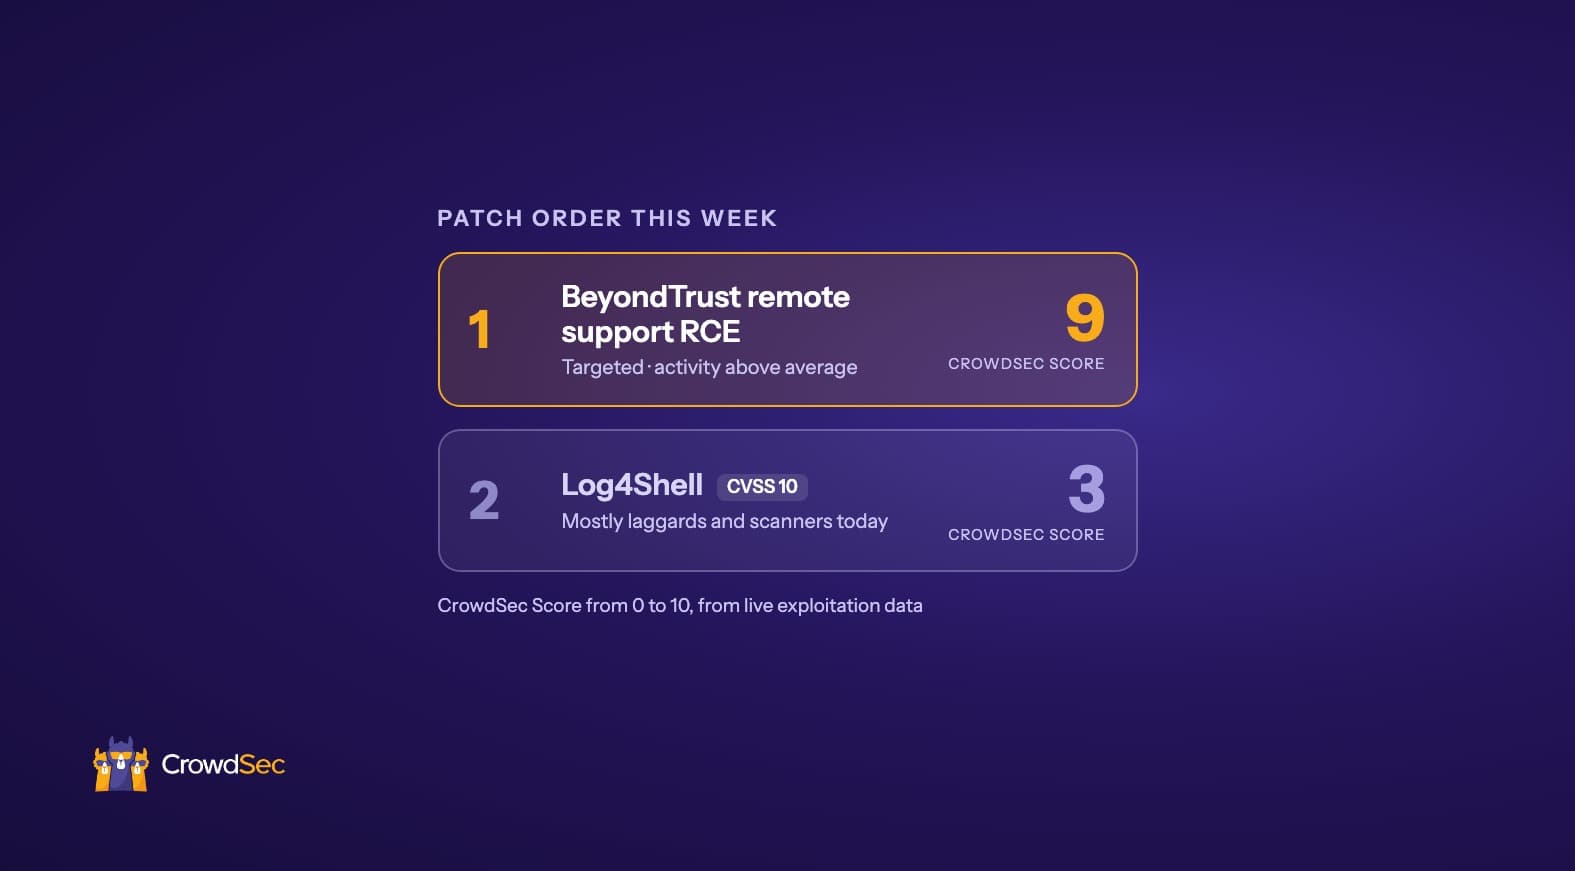
- CrowdSec enables you to prioritize with real-world exploitation evidence from production telemetry.
Practical workflows defenders can build today
Here are a few high-impact ways teams can combine these approaches:
Closing thoughts
We welcome db.gcve.eu as a concrete, open, European-operated contribution to a more resilient vulnerability intelligence ecosystem, one that values interoperability, multi-source correlation, and open access.
And we’ll keep pushing the complementary idea that defenders deserve more than static scores: they deserve real-time, accurate information about attackers so they can prioritize, mitigate, and stay ahead.
Finally, visit db.gcve.eu to learn more.