Pre-NVD: what attackers probe before the CVE exists
Attackers probe products weeks before a CVE reaches the NVD. What pre-NVD detection is, what it catches, and how to block scanners before a patch exists.
Proactive Cybersecurity
How to prioritise CVEs by real exploitation, beyond CVSS, EPSS and KEV
CVSS, EPSS and KEV estimate risk. To prioritise patching, check if a CVE is exploited now, how targeted it is and whether it’s growing. A practical method.
Proactive Cybersecurity
What 300,000 Security Engines saw: 8 lessons on exploitation from SANS 2026
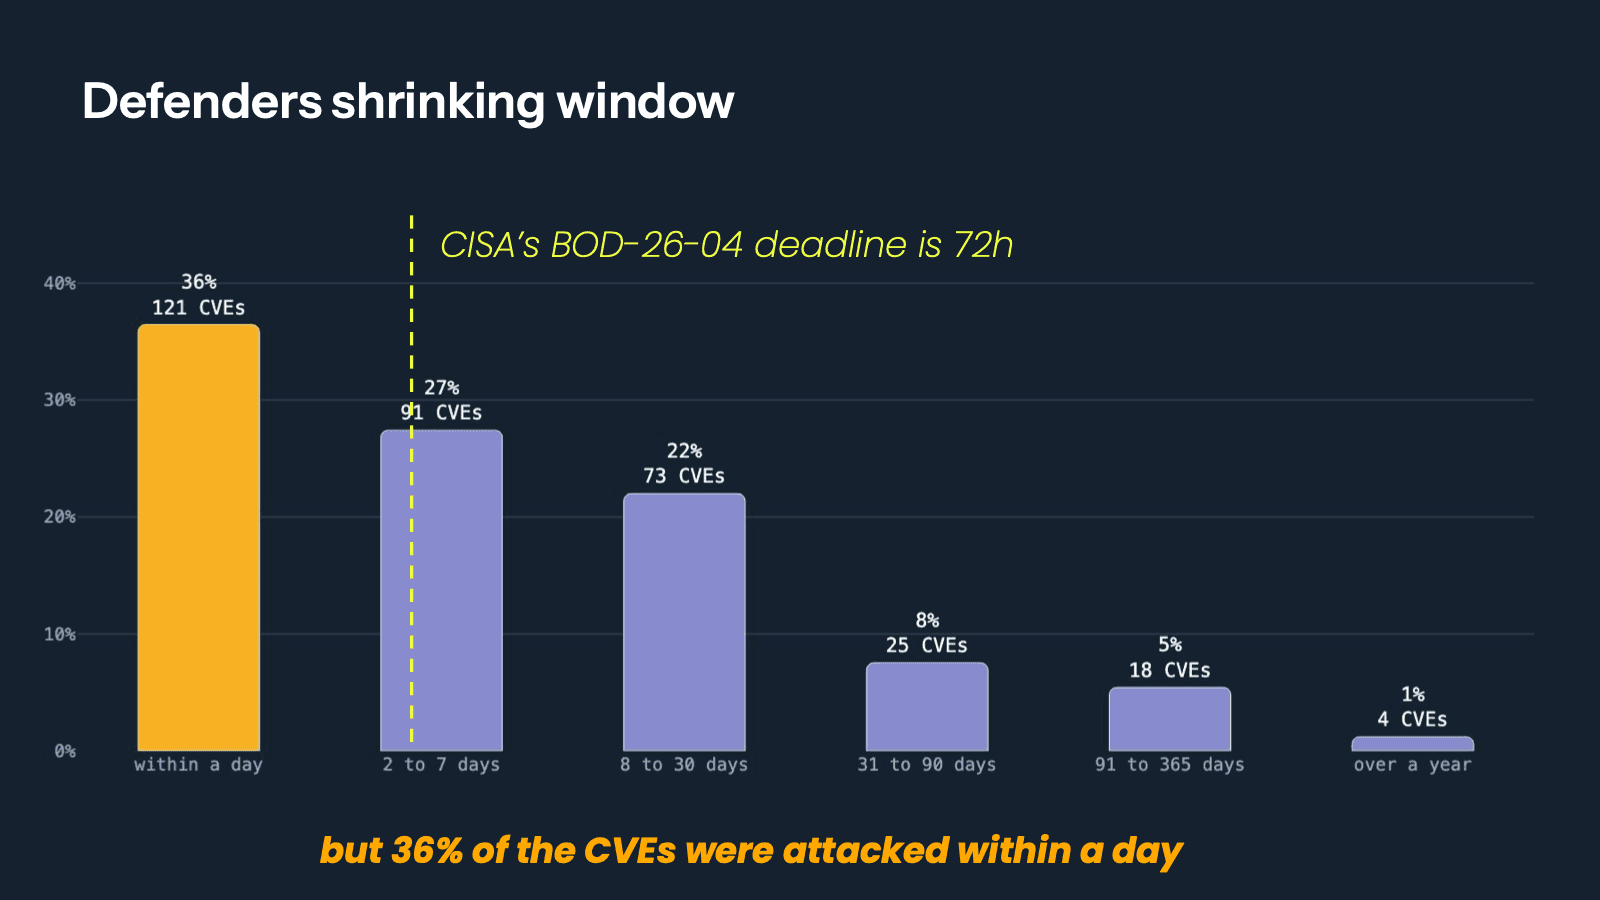
36% of exploited CVEs were attacked within a day of publication. What 300,000 Security Engines saw at SANS 2026: borrowed cloud IPs, early zero-days, old CVEs.
Proactive Cybersecurity
IP reputation vs full CTI: what your SOC actually needs
Most SOCs need fast IP reputation in their SIEM before they need attribution-heavy CTI. How to tell them apart, and what to ask any IP reputation vendor.
AI
How to Block Bots, Headless Browsers, and Scrapers on Nginx with CrowdSec
Set up open-source Nginx bot protection with CrowdSec to block scrapers, headless browsers, AI crawlers, and other unwanted automated traffic.
AI
What’s New in CrowdSec 1.8: WAF Bot Detection, Kubernetes Datasource, and Performance Improvements
Discover what’s new in CrowdSec 1.8, including WAF bot detection, a dedicated Kubernetes datasource, faster LAPI synchronization, and improved Console alerts.
AI
Why You Should Write a Skill for Your Software
Learn why AI agent skills make software setup more reliable, reduce LLM guesswork, improve troubleshooting, and can even expose gaps in your documentation.
Integrations
WAF for Traefik with CrowdSec: Virtual Patching in Docker
Add an open-source WAF to Traefik with CrowdSec. Wire the bouncer plugin, enable virtual patching, and block real attacks, step by step in Docker.
Integrations
Open-Source WAF for Nginx on Ubuntu with CrowdSec
Deploy an open-source WAF for Nginx on Ubuntu with CrowdSec. Install the AppSec component, enable virtual patching, and block attacks step by step
Proactive Cybersecurity
CISA gives you 3 days to patch and triage. Live Exploit Tracker gives you a head start
CISA BOD 26-04 mandates risk-based patching driven by real exploitation evidence. Live Exploit Tracker delivers that evidence live — per CVE, per vendor.
CrowdSec
Edge is the new endpoint: How to respond when edge CVEs go hot
Edge CVEs move fast from disclosure to exploitation. Learn a practical 60-minute response framework to assess exposure, reduce risk, deploy mitigations, and communicate clearly during edge vulnerability incidents.
Learn the difference between vulnerabilities, threats, and risks, and how understanding their lifecycle helps prevent security incidents.
Proactive Cybersecurity
CrowdSec Welcomes db.gcve.eu, Strengthening Europe’s Vulnerability Intelligence, Without Losing Global Interoperability
Strengthen your vulnerability workflows with db.gcve.eu: aggregated advisories, cross-source correlation, & real-time exploitation insights from CrowdSec.
Proactive Cybersecurity
5 Common Vulnerability Myths That Put Your Security At Risk
Discover 5 common cybersecurity myths that increase risk, from “we’re too small” to CVSS blind spots. Learn what really reduces exposure.
Proactive Cybersecurity
Honeypots vs Production Telemetry: What CISOs Should Trust for Threat Intelligence
Threat intelligence isn’t equal. Learn why real-world production telemetry reveals attacker intent, and why CISOs trust it over honeypot-based intel.
Inside CrowdSec
Secure Kubernetes Ingress with CrowdSec and Traefik: WAF, Virtual Patching, and DevSecOps at Scale
Learn how to secure Kubernetes ingress with Traefik & CrowdSec. Enable open-source WAF, virtual patching, & DevSecOps-friendly protection for web-native workloads.
Inside CrowdSec
DevSecOps Without Friction: How CrowdSec Fits Your Pipelines and Your Perimeter
CrowdSec enhances DevSecOps with behavior-based detection and edge filtering. Strengthen security without slowing pipelines.
Announcement
Protecting FOSS Communities from AI Crawlers with Free CrowdSec Blocklist
Announcing free access to the CrowdSec AI Crawlers Blocklist for all open source projects, to help FOSS communities reduce unwanted traffic from AI bots.
Ambassador Post
Implementing the CrowdSec WAF for Advanced Web Application Security
Transform your Security Engine into a WAF with this get-started guide and learn how to integrate and configure the AppSec Component with NGINX on Debian 12.
Announcement
Protect Your Digital Assets Against AI Crawlers
Let’s explore some of the most abusive AI crawler behaviors and learn how to block them using the CrowdSec AI Crawlers Blocklist.
Announcement
Multimodal Offensive AI: The Next Frontier in Offensive AI and A Wake-Up Call for Cybersecurity
The Multimodal Offensive AI ebook explores the next evolutionary step of offensive AI. Understand this next evolution of cyber threats and how you can prepare.